International Cyber Expo International Cyber Expo
  • About Us
Thursday, 22 October, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

HP Device Manager has a dangerous backdoor

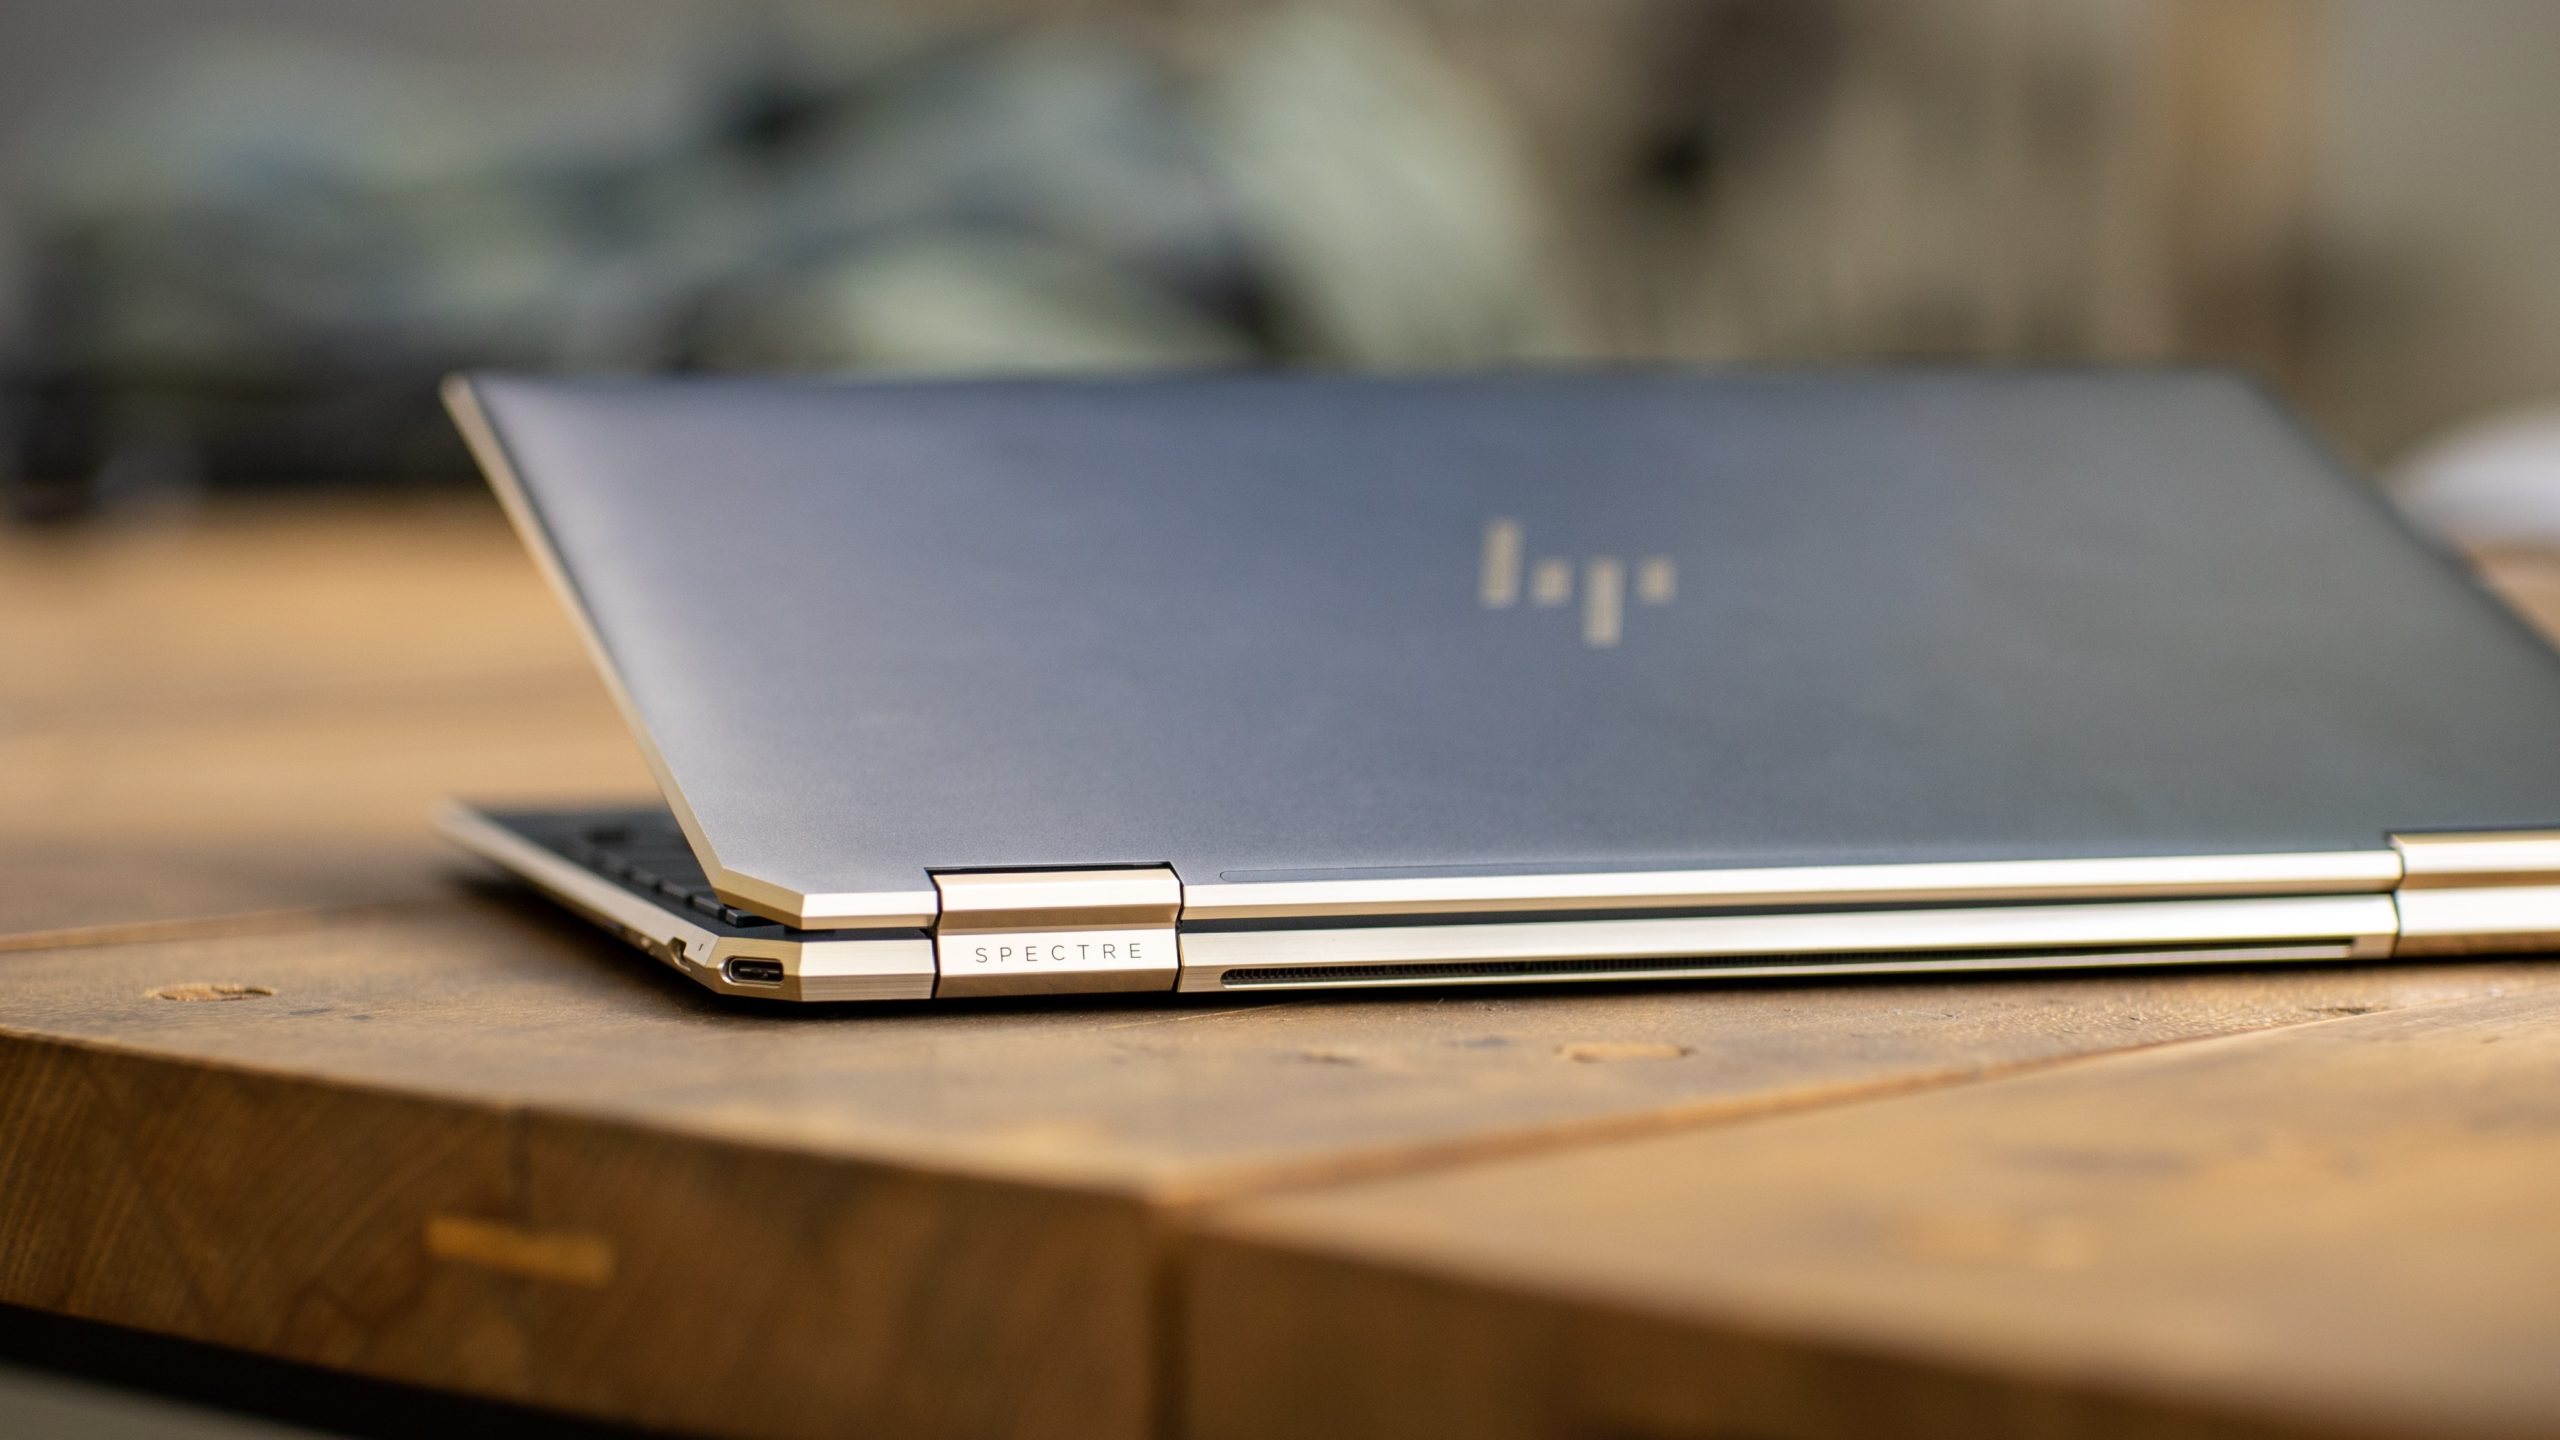
HP Device Manager has an open backdoor which allows anyone on your networks to become an admin to your server

by The Gurus
September 30, 2020
in Cyber Bites
HP Thin
Share on FacebookShare on Twitter

HP Device Manager is a popular software that allows IT administrators to manage their HP Thin Client devices. However, it has a backdoor database user account which can undermine the network security.

Founder of Cognitous Cyber Security, Nick Bloor, discovered that an insecure user account had been set-up by an HP Inc programmer in a database within HP Device Manager. He found that the account can be easily exploited by malicious users to achieve privilege escalation to gain unauthorized remote command execution as SYSTEM.

The issue with this flaw is that if a vulnerable installation of this device manager on a network can be reached, then a user can gain admin-level control of the machine, as well as the thin clients it controls.  Bloor said that “anyone with access to a server where HP Device Manager is installed could use this user account to gain complete control over the server,” which qualifies as local privilege escalation. Bloor has confirmed that the vulnerability exists in the current version of HP Device Manager, but cannot confirm this on past versions. Since the incident, HP has released an advisory alert for customers.

ShareTweet
Previous Post

Universal Health Services hit by ransomware attack

Next Post

Major watch maker, Swatch hit with cyberattack

Recent News

Critical PHP Vulnerabilities Spark Global Security Alert: Industry Experts React

Critical PHP Vulnerabilities Spark Global Security Alert: Industry Experts React

October 22, 2026
Huntress Expands Ingram Micro Partnership Across Canada and Latin America

Huntress Expands Ingram Micro Partnership Across Canada and Latin America

October 22, 2026
DOQEX Achieves Cyber Essentials Certification to Strengthen Security Standards

DOQEX Achieves Cyber Essentials Certification to Strengthen Security Standards

October 22, 2026
Exposed Refrigeration Systems Raise Global Cybersecurity Concerns

Exposed Refrigeration Systems Raise Global Cybersecurity Concerns

October 22, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol