International Cyber Expo International Cyber Expo
  • About Us
Wednesday, 7 October, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

Recent ransomware attacks prompt action from two-thirds of companies

by Guru Writer
May 26, 2021
in Cyber Bites
ransomware
Share on FacebookShare on Twitter

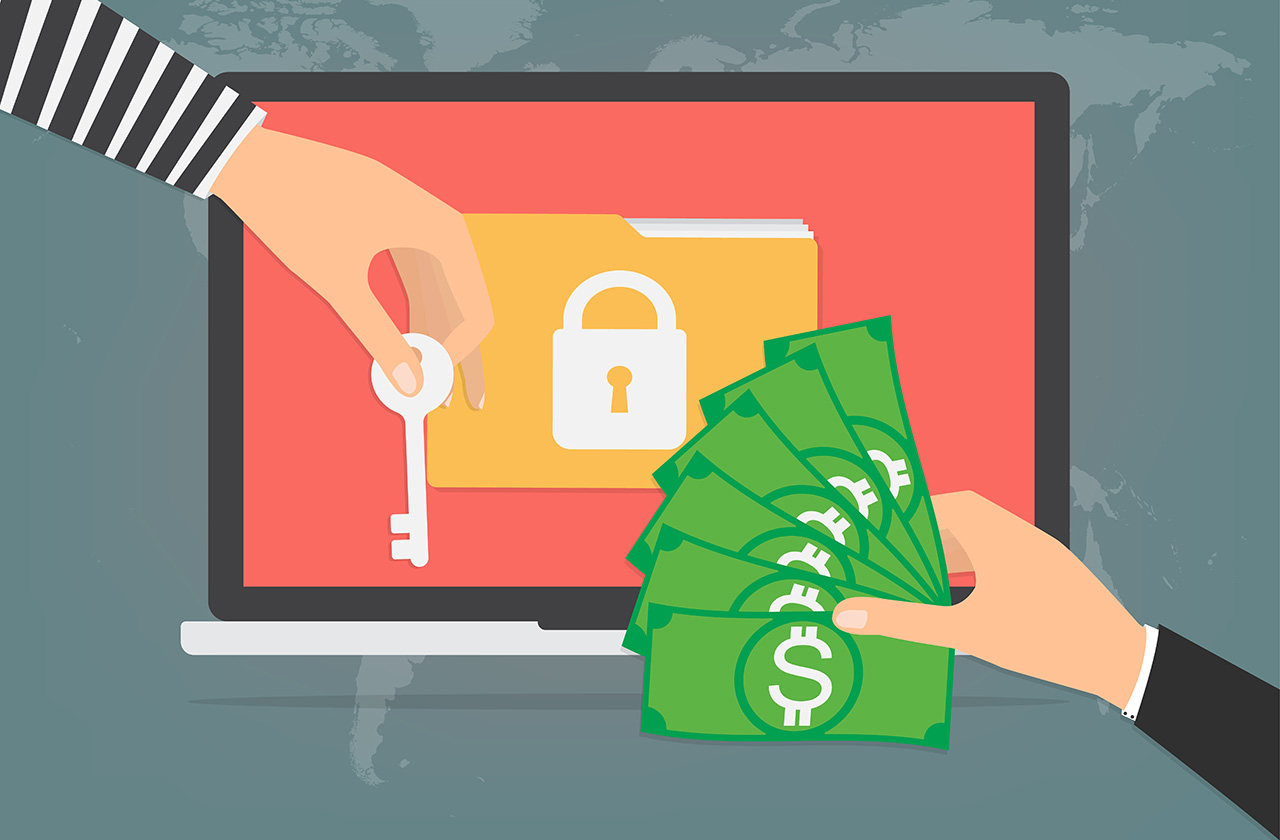
In the aftermath of the Colonial Pipeline attack, global IT association and learning community ISACA polled more than 1,200 members in the United States and found that 84 percent of respondents believe ransomware attacks will become more prevalent in the second half of 2021. According to the report, the severe disruptions caused by these attacks has been noted by organisations, along with the requirement to bolster defences against cyberattacks. In fact, over two-thirds are set to take action to prevent them becoming another ransomware victim following the incident.

And though Colonial reportedly authorised a ransom payment of US $4.4 million, in the ISACA survey, four out of five respondents said they do not think their organisation would pay the ransom. And only 22 percent said a critical infrastructure organisation should pay the ransom if attacked.


“In a vacuum, the guidance not to pay makes total sense. We don’t want to negotiate with criminals,” said Dustin Brewer, senior director of emerging technology and innovation at ISACA. “But when you need to get your business back online, a cost/benefit analysis is going to come into play, and a company is going to do what it needs to do to have continuity. Good cyber-hygiene has to be a focus to avoid getting to this point.”

ShareTweet
Previous Post

One Identity Doubles Down on its Cloud-First Strategy

Next Post

VMware issues critical patch on vCenter Server installs

Recent News

Power BI phishing campaign drops rogue ScreenConnect clients

Power BI phishing campaign drops rogue ScreenConnect clients

October 7, 2026
The trust gap that AI watermarking can’t close

The trust gap that AI watermarking can’t close

October 7, 2026
Middle managers want tighter human oversight of AI than their bosses, TeamViewer research finds

Middle managers want tighter human oversight of AI than their bosses, TeamViewer research finds

October 7, 2026
Verify it, don’t assume it: why untested security controls are making life easy for attackers

Verify it, don’t assume it: why untested security controls are making life easy for attackers

October 7, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol