International Cyber Expo International Cyber Expo
  • About Us
Thursday, 17 September, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

Two in Five Organisations Hit by AI-Related Compliance Failures in Past Year, Research Finds

by Lara Joseph
September 17, 2026
in AI and Machine Learning, News
Two in Five Organisations Hit by AI-Related Compliance Failures in Past Year, Research Finds
Share on FacebookShare on Twitter

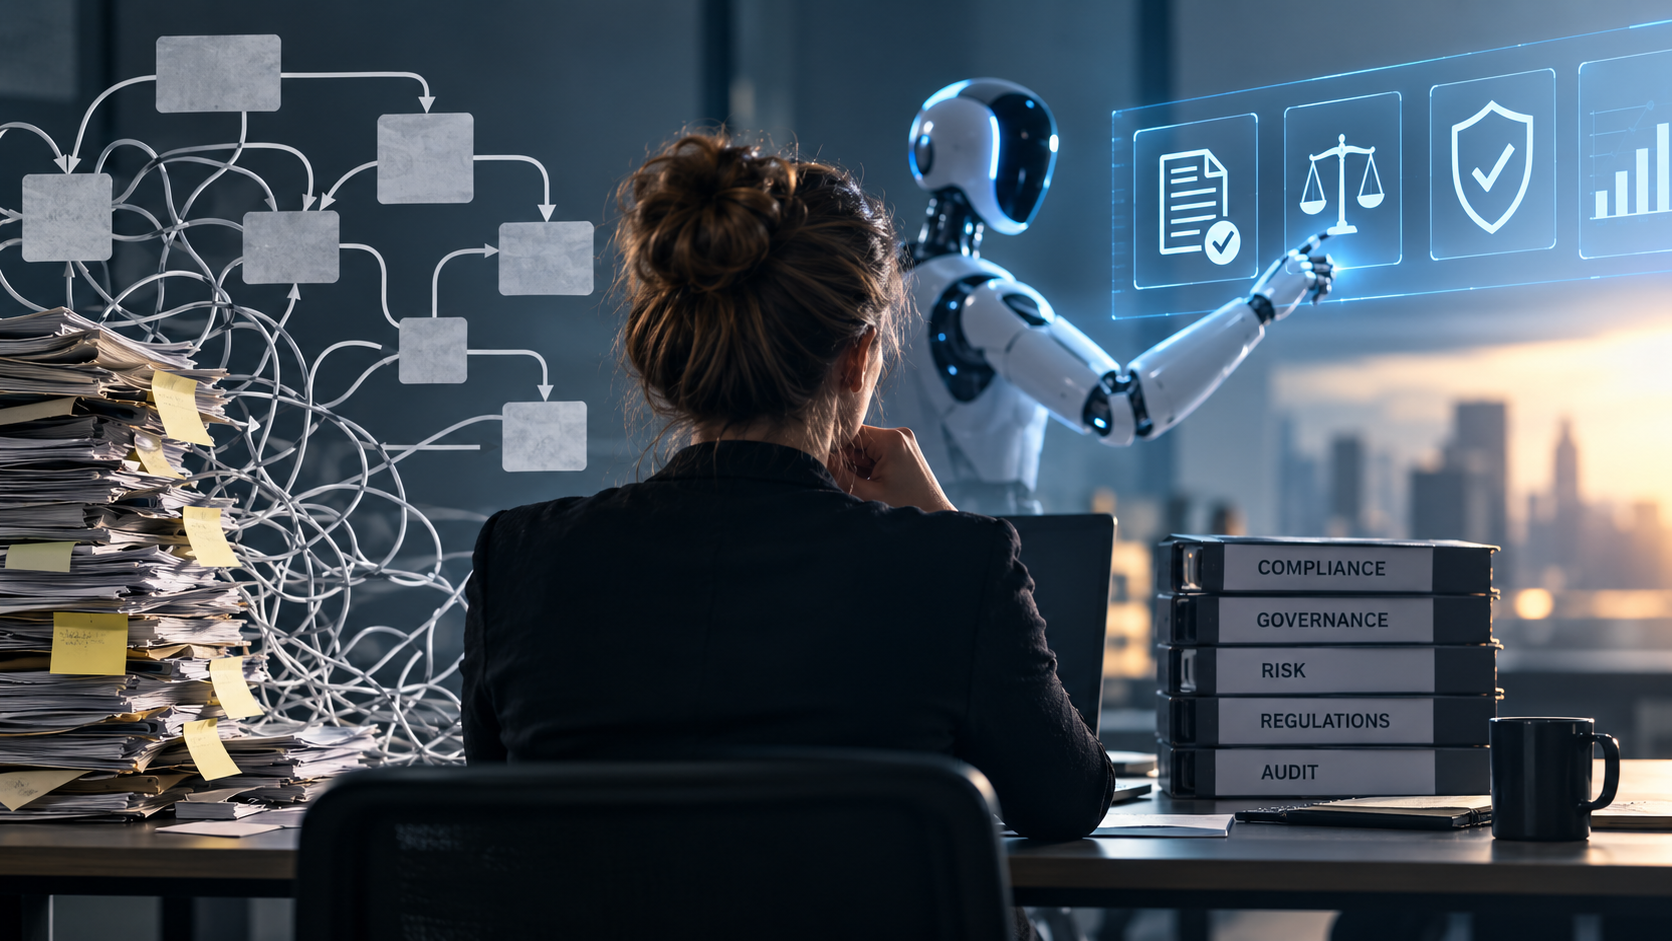
40% of organisations have suffered an AI-related compliance or governance issue in the last 12 months, with legacy and poorly designed business processes identified as the leading cause, according to new research from Camunda.

The study found that process-related issues contributed to 84% of the compliance and governance failures organisations reported. Employees appear acutely aware of the risk: 79% said they fear their own use of AI could trigger a compliance issue at their organization, while 96% expect process-related challenges to fuel future AI compliance problems.

Almost half of organisations (48%) also expressed concern about AI agents “going rogue” if they are allowed to make changes to a process, reflecting broader anxiety about handing autonomous systems control of operational workflows.

A gap between adoption and governance

The findings, published in Camunda’s report The AI Process Gap, point to a widening gulf between the pace of AI adoption and organizations’ ability to govern it. Daniel Meyer, CIO at Camunda, said the more pressing danger isn’t runaway AI agents but organizations failing to adapt their own operations quickly enough.

“There is a lot of debate about rogue AI agents and whether innovation is moving too fast. But the more immediate risk is that many organisations are not changing the way they work fast enough to keep pace with AI,” Meyer said. He warned that bolting AI onto processes “designed for a pre-AI world” has created a dangerous gap between adoption speed and governance strength, leaving organizations more exposed to compliance failures, regulatory scrutiny and costly penalties.

The cost of broken processes

The report quantifies the fallout: 72% of organisations say process-related challenges have already caused AI initiatives to fail outright, at an average cost of $1.55 million per business. A further 72% believe AI costs will spiral unless organisations gain tighter control over their business processes, and 82% think their AI investments will ultimately be a bust without heavier investment in process redesign.

Despite this, most organisations are taking the path of least resistance. Rather than rebuilding processes from the ground up around AI, 79% say simply layering AI onto existing workflows generates less internal pushback, even though 82% acknowledge that adapting all their critical processes for AI could take up to five years.

Kurt Petersen, SVP Customer Success at Camunda, said the pattern is a predictable source of disappointing returns. “Organisations are rapidly adopting AI. But they are applying it to processes designed for a world before AI, then wondering why the return on investment falls short,” Petersen said. He noted that 61% of respondents say business process redesign simply cannot keep pace with the speed at which they need to move on AI, pushing many teams toward “the quick fix of bolting AI onto processes that were never built for it.” Processes designed before the AI era, he added, “cannot support the technology effectively without being re-engineered, no matter how much is spent on agents and models.”

ShareTweet
Previous Post

World Quantum Readiness Day: Industry Voices on Moving From Blueprint to Build

Recent News

Two in Five Organisations Hit by AI-Related Compliance Failures in Past Year, Research Finds

Two in Five Organisations Hit by AI-Related Compliance Failures in Past Year, Research Finds

September 17, 2026
World Quantum Readiness Day: Industry Voices on Moving From Blueprint to Build

World Quantum Readiness Day: Industry Voices on Moving From Blueprint to Build

September 17, 2026
6 Ways Security Teams Can Reduce Non-Human Insider Risk

6 Ways Security Teams Can Reduce Non-Human Insider Risk

September 17, 2026
CSIDES Unveils Full Agenda for 2026 Cybersecurity Community Event

CSIDES Unveils Full Agenda for 2026 Cybersecurity Community Event

September 17, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol