International Cyber Expo International Cyber Expo
  • About Us
Wednesday, 30 September, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

Attacker signs up as a member to plant webshells on parks and recreation platform, hunts for card data

by Guru Writer
September 30, 2026
in News
Attacker signs up as a member to plant webshells on parks and recreation platform, hunts for card data
Share on FacebookShare on Twitter

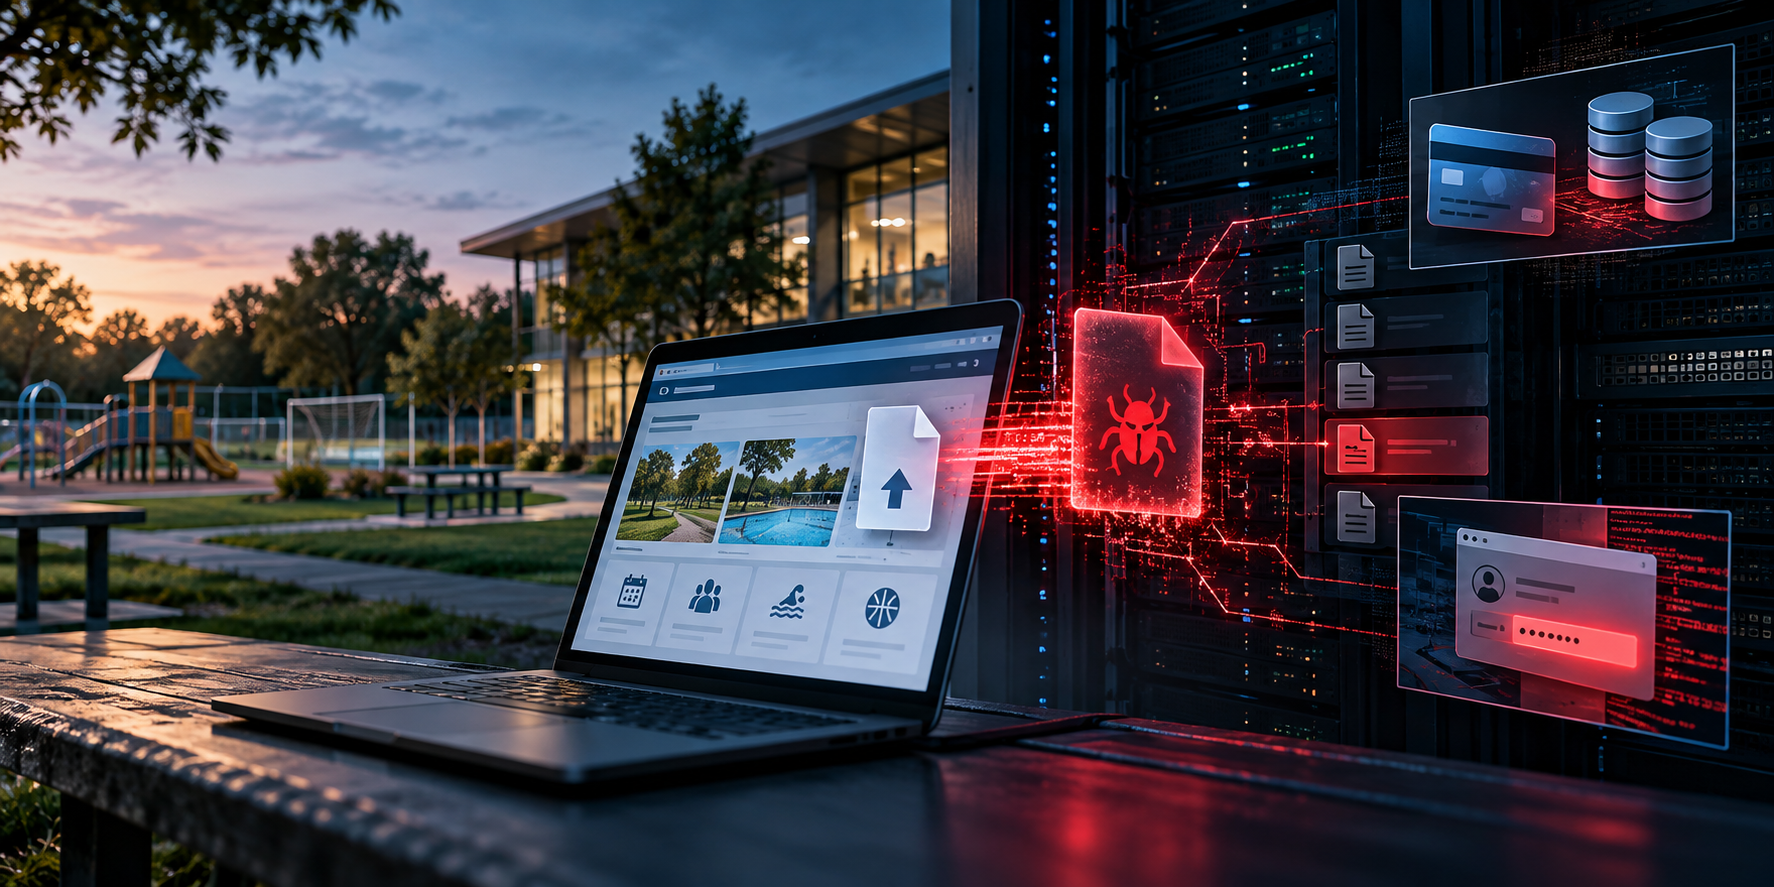
Security researchers at Huntress have detailed a multi-stage intrusion in which a threat actor compromised three web servers belonging to a popular recreation management platform used by local municipalities and parks organisations, planting webshells and going after payment card data.

The activity, first observed on 10 September 2026, began noisily. Over roughly six hours the attacker threw a string of unauthenticated techniques at the first server, including brute-forcing the admin and member login pages, IIS 8.3 tilde enumeration, WebDAV method abuse and upload-handler parser bypasses. None of them worked.

What did work was far simpler. The attacker registered a new member account and abused the platform’s member file upload feature to drop .aspx webshells into a publicly reachable documents directory. From there they carried out reconnaissance, pulled the global IIS configuration file and searched web.config and C# source files for connection strings, passwords and API keys.

With database credentials in hand, the motive became clear. The attacker searched the environment for card-related strings and payment provider names, then dumped webhook logs from a payment integration to extract card numbers, expiry dates and CVVs.

Quieter, then stealthier

The same technique was used on a second server, this time with far less noise, before Huntress’s SOC removed the webshells. On the third server the attacker changed tactics again, copying their webshells into innocuous-looking locations under names such as css_bundle.aspx and webresource.aspx and timestomping the files so their metadata matched legitimate site components. An attempt to plant further copies inside the platform’s payment module directories failed.

The most serious phase came when the third server was put back into production before it had been fully secured. Using the account they had already registered, the attacker returned and ran PowerShell “planter” scripts that appended an obfuscated dropper to a legitimate jQuery file loaded by the platform’s authentication page. The trojanised script pulled a second-stage browser agent hosted on Cloudflare Workers and opened encrypted WebRTC and WebSocket channels, designed to harvest users’ credentials in real time.

AI fingerprints

Huntress says a zh-CN locale in the attacker’s PowerShell user-agent string suggests the actor is most likely based in China. The researchers also believe AI-generated scripts were used across the kill chain, from the high volume of early access attempts to the final PowerShell scripts, whose comments appear to include fragments of the instructions given to the AI.

ShareTweet
Previous Post

CyberASAP Celebrates 10th Anniversary with Special Event Exploring Future of UK Cyber Security Innovation

Recent News

Attacker signs up as a member to plant webshells on parks and recreation platform, hunts for card data

Attacker signs up as a member to plant webshells on parks and recreation platform, hunts for card data

September 30, 2026
CyberASAP Secures £10m Boost as UK’s Next Wave of Cyber Innovators Take Centre Stage

CyberASAP Celebrates 10th Anniversary with Special Event Exploring Future of UK Cyber Security Innovation

September 30, 2026
Continuous Penetration Testing: Why Annual Pen Tests Are a Compliance Checkbox, Not a Security Strategy

Continuous Penetration Testing: Why Annual Pen Tests Are a Compliance Checkbox, Not a Security Strategy

September 30, 2026
AI Is Making Software Cheaper to Attack. Defenders Need to Change the Price

AI Is Making Software Cheaper to Attack. Defenders Need to Change the Price

September 30, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol