International Cyber Expo International Cyber Expo
  • About Us
Friday, 9 October, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

Attackers exploit AhsayCBS backup flaws to deploy disguised crypto miners

by Guru Writer
October 9, 2026
in News
Attackers exploit AhsayCBS backup flaws to deploy disguised crypto miners
Share on FacebookShare on Twitter

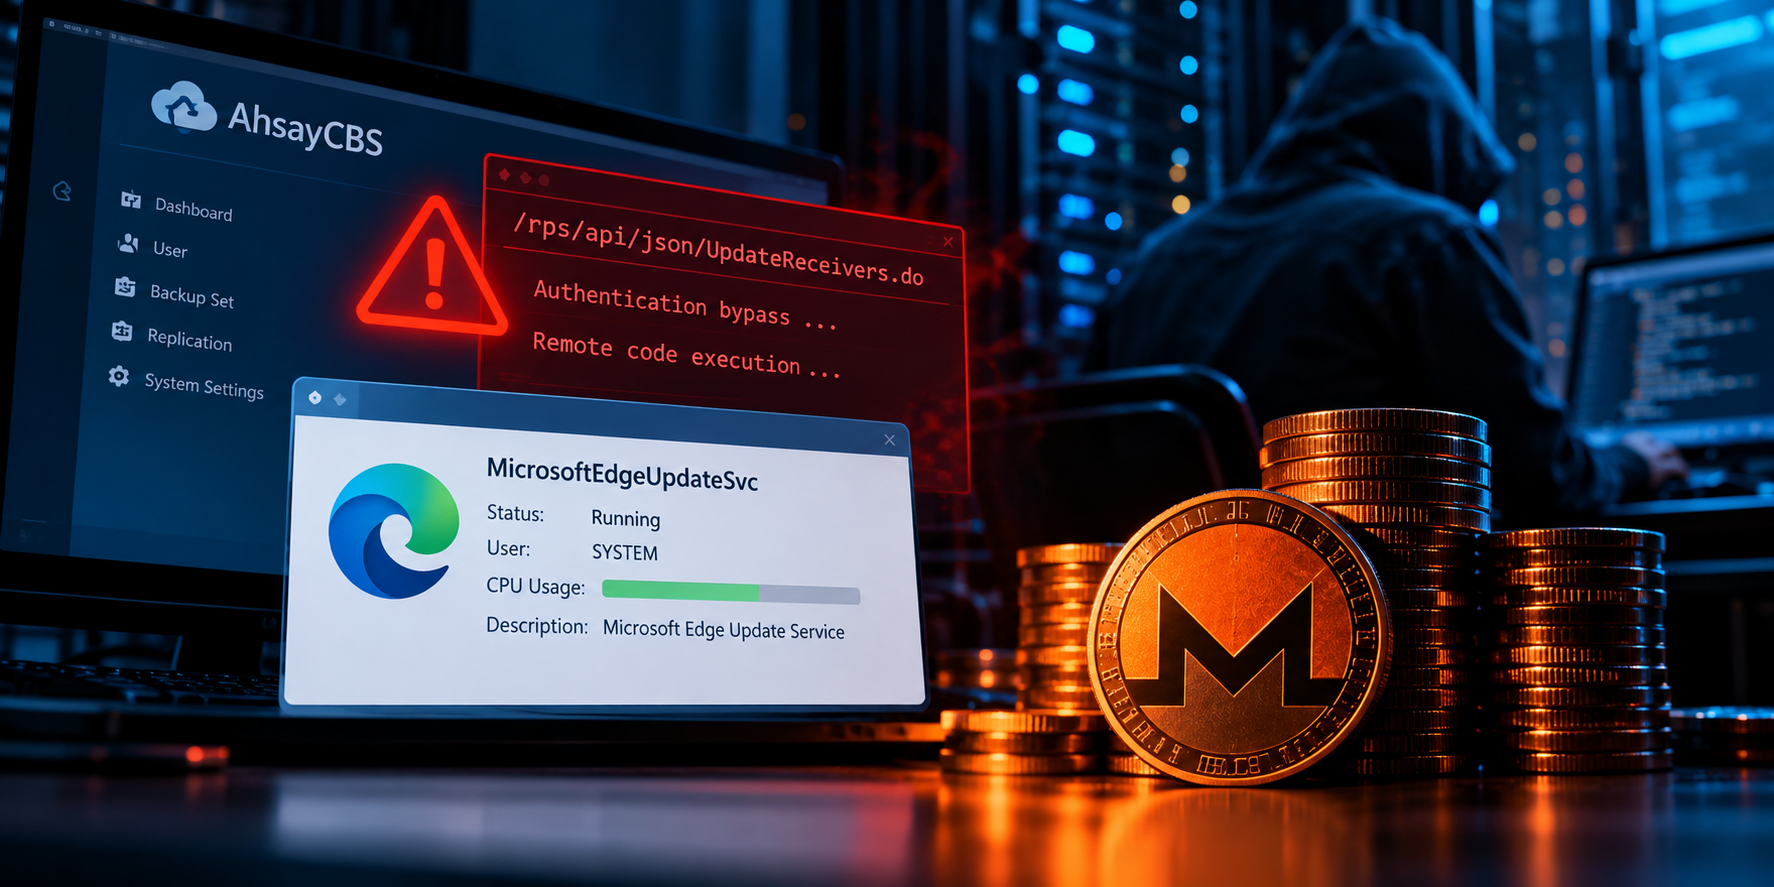
Attackers are exploiting two newly disclosed vulnerabilities in AhsayCBS, the management console for Ahsay’s cloud backup software, to take over servers and quietly run cryptocurrency miners, according to researchers at Huntress.

AhsayCBS (Cloud Backup Server) is mainly used by managed service providers (MSPs) and system integrators to create users and manage backup policies for their clients. As of 8 October, Huntress had seen five organisations targeted via the flaws.

From disclosure to exploitation in three days

The two vulnerabilities, CVE-2026-105133 and CVE-2026-105134, were published to the US National Vulnerability Database (NVD) on 4 October. Huntress began seeing exploitation attempts on 7 October at 23:20 UTC.

CVE-2026-105133 is a medium-severity flaw in the checkSysPwd function that can lead to improper authentication. CVE-2026-105134 is a critical-severity vulnerability in the /rps/api/json/UpdateReceivers.do endpoint of the Replication Receiver component. It contains an authentication bypass that allows a random token to stand in for valid credentials, leading to unauthenticated remote code execution as NT AUTHORITY\SYSTEM.

Attackers chained the two flaws, first bypassing authentication and then gaining code execution. They configured a malicious replication receiver and dropped a JSP webshell into the application directory served by CBS. Huntress first spotted the activity through suspicious command lines spawned by the cbssvcX64.exe service.

Versions up to 10.3.2 are affected. Version 10.3.4, released on 5 August, is not vulnerable.

A miner in disguise

Once inside, the attackers downloaded a set of payloads from an Alibaba Cloud object storage host. These included an XMRig Monero miner disguised as Microsoft Edge (edge.exe), and a modified copy of the NSSM service utility (msedge.exe). The attackers used it to run the miner as a SYSTEM-level service named MicrosoftEdgeUpdateSvc, mimicking the genuine Edge update service. The miner connected to a Monero mining pool on port 8029.

A PowerShell script, Taskgmr.ps1, was used to help the miner avoid detection. If Task Manager was opened, the script stopped the fake Edge service to hide the mining activity. It also killed Task Manager at 18:00, as well as whenever it had been left open for more than an hour overnight, based on the endpoint’s local clock rather than UTC. Huntress said the script appears to be AI-assisted, given its commented code.

In one incident, the attackers also loaded WinRing0x64.sys, a legitimate but vulnerable kernel driver. Huntress noted that attackers often use vulnerable drivers to disable endpoint security tools. In this case, loading the driver gave the miner kernel-level access to the hardware.

[Optional: approved spokesperson quote to be inserted here]

What defenders should do

Huntress is urging organisations running AhsayCBS to:

  • Upgrade to version 10.3.4 immediately.
  • Restrict access to the AhsayCBS management web interface to trusted IP addresses only, or require VPN access.
  • Fully re-image any compromised host from a trusted backup, as attackers may have left additional backdoors.
  • Deploy the Sigma detection rules and block the indicators of compromise published by Huntress, including the mining pool, payload URLs and file hashes.

Huntress said it is working with potentially affected organisations across its customer base to apply these mitigations.

Full research, including indicators of compromise and detection rules: https://www.huntress.com/blog/ahsaycbs-flaws-exploit

ShareTweet
Previous Post

WorkNest Secure Achieves CREST STAR-FS Accreditation for Red Teaming

Recent News

Attackers exploit AhsayCBS backup flaws to deploy disguised crypto miners

Attackers exploit AhsayCBS backup flaws to deploy disguised crypto miners

October 9, 2026
WorkNest Launches WorkNest Secure to Expand Cybersecurity and Compliance Services

WorkNest Secure Achieves CREST STAR-FS Accreditation for Red Teaming

October 8, 2026
Global cyber attacks up 48% as ransomware and phishing climb, Check Point finds

Global cyber attacks up 48% as ransomware and phishing climb, Check Point finds

October 8, 2026
Filigran event

Filigran announces speakers for first THREAD event

October 8, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol