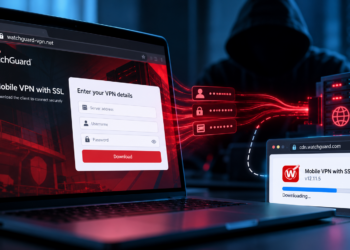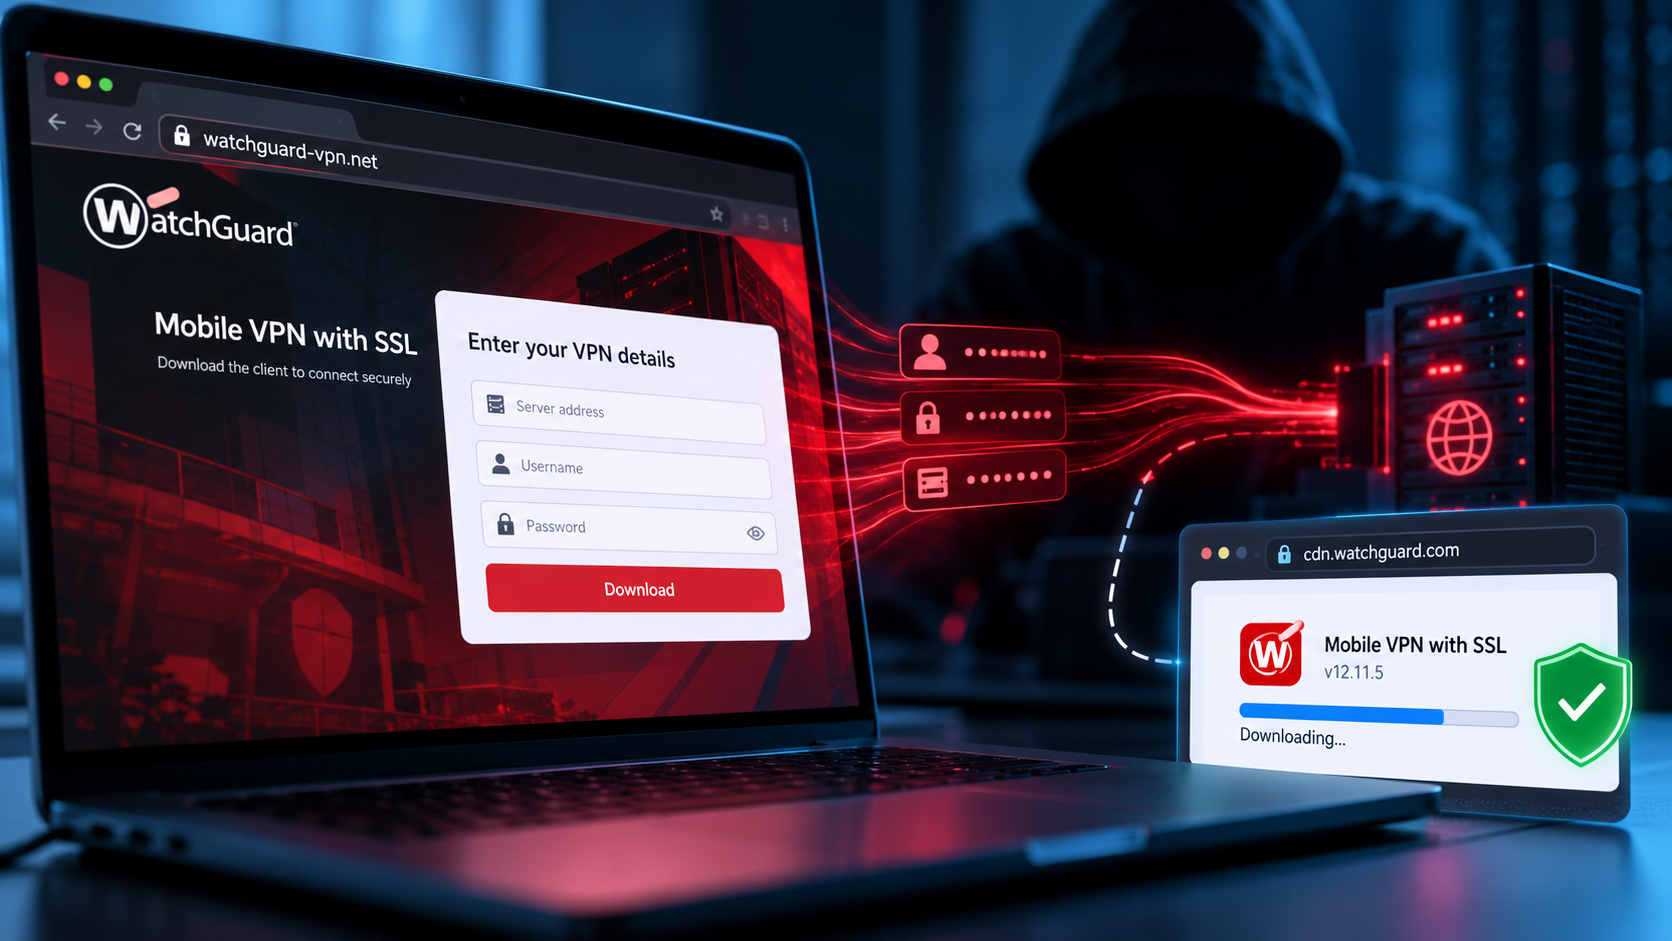
Huntress researchers have uncovered an SEO-poisoning campaign that harvests SSL VPN credentials through a lookalike WatchGuard download page, then hands victims the real, validly signed installer from WatchGuard’s own CDN, leaving endpoint tools with nothing to detect.

The activity, detailed by the Huntress SOC on 13 October, centres on watchguard-vpn[.]net, a lookalike domain posing as a download page for WatchGuard’s Mobile VPN with SSL client. Unlike earlier waves of the campaign, which relied on trojanised installers, this iteration strips the malware out entirely.
A typo and a search result
The incident Huntress investigated began on 7 October, when an administrator at a managed service provider searched Bing for “watchguard vpn sll download”. Eight seconds later they had clicked through to the fake site via a standard Bing result redirect, which Huntress says points to SEO poisoning rather than malvertising.
Two bites at the password
Clicking any download option on the site opens a pop-up asking for the VPN server address, username and password, the same three values the legitimate client requests. The logic sits in roughly 150 lines of unobfuscated JavaScript (popup.js), which posts the entries as JSON to a separate collection domain, watchguard-ssl[.]online.
The first submission is always rejected with an “incorrect data” message, prompting victims to retype carefully or try a different password. That gives the operators a second, likely more accurate, set of credentials, along with the server address they need to log in.
The payload is the real thing
After the second submission, the script triggers a download of WatchGuard’s genuine Mobile VPN with SSL installer (version 12.11.5) direct from cdn.watchguard.com. Huntress verified the file’s Authenticode signature from WatchGuard Technologies and confirmed the binary had not been altered.
With no trojanised MSI or sideloaded DLL in the chain, there is nothing for EDR to flag, and the victim gets exactly the install they expected. Detection was thin across the board: as of 8 October only seven VirusTotal vendors flagged the lure domain and two flagged the collector.
Old domain, new backend
WatchGuard’s Secplicity team first reported watchguard-vpn[.]net in January as part of a wider credential-harvesting campaign spoofing WatchGuard, F5, Fortinet, SonicWall and Sophos clients, though at that point the domain had no working backend. Microsoft later attributed related activity to Storm-2561, a financially motivated actor active since May 2025. WHOIS data shows the domain was registered again on 22 August, with the collector domain following on 14 September. Huntress says it cannot establish whether the same operators controlled both registrations.
In the case investigated, Huntress flagged the activity 21 seconds after the site loaded, and browser history suggests the user did not complete both rounds. The domain was offline as of 13 October, and Huntress has shared infrastructure details with WatchGuard.
Recommendations
- Reset passwords for any account entered on the site and treat the associated VPN endpoint as known to the attacker.
- Enforce MFA on SSL VPN access.
- Monitor for VPN logins from hosting providers, unfamiliar ASNs or new countries.
- Block watchguard-vpn[.]net, watchguard-ssl[.]online, 80.249.132[.]140 and 158.94.209[.]19.
- Publish and bookmark official download links such as software.watchguard.com.
Full research: https://www.huntress.com/blog/fake-watchguard-vpn-credential-phishing