International Cyber Expo International Cyber Expo
  • About Us
Wednesday, 18 November, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2027
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2027
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

Token-replay campaign hijacks 97 Microsoft 365 accounts as Huntress extends SOC response across Defender

by Guru Writer
November 18, 2026
in News
Token-replay campaign hijacks 97 Microsoft 365 accounts as Huntress extends SOC response across Defender
Share on FacebookShare on Twitter

Huntress has expanded its Agentic Security Platform so that its 24/7 security operations centre (SOC) can investigate and respond to incidents raised across the wider Microsoft Defender suite, not only Defender for Endpoint and Defender Antivirus.

The move follows a token-replay campaign that Huntress tracked between 14 July and 22 September 2026, which compromised 97 Microsoft 365 accounts across 79 organisations.

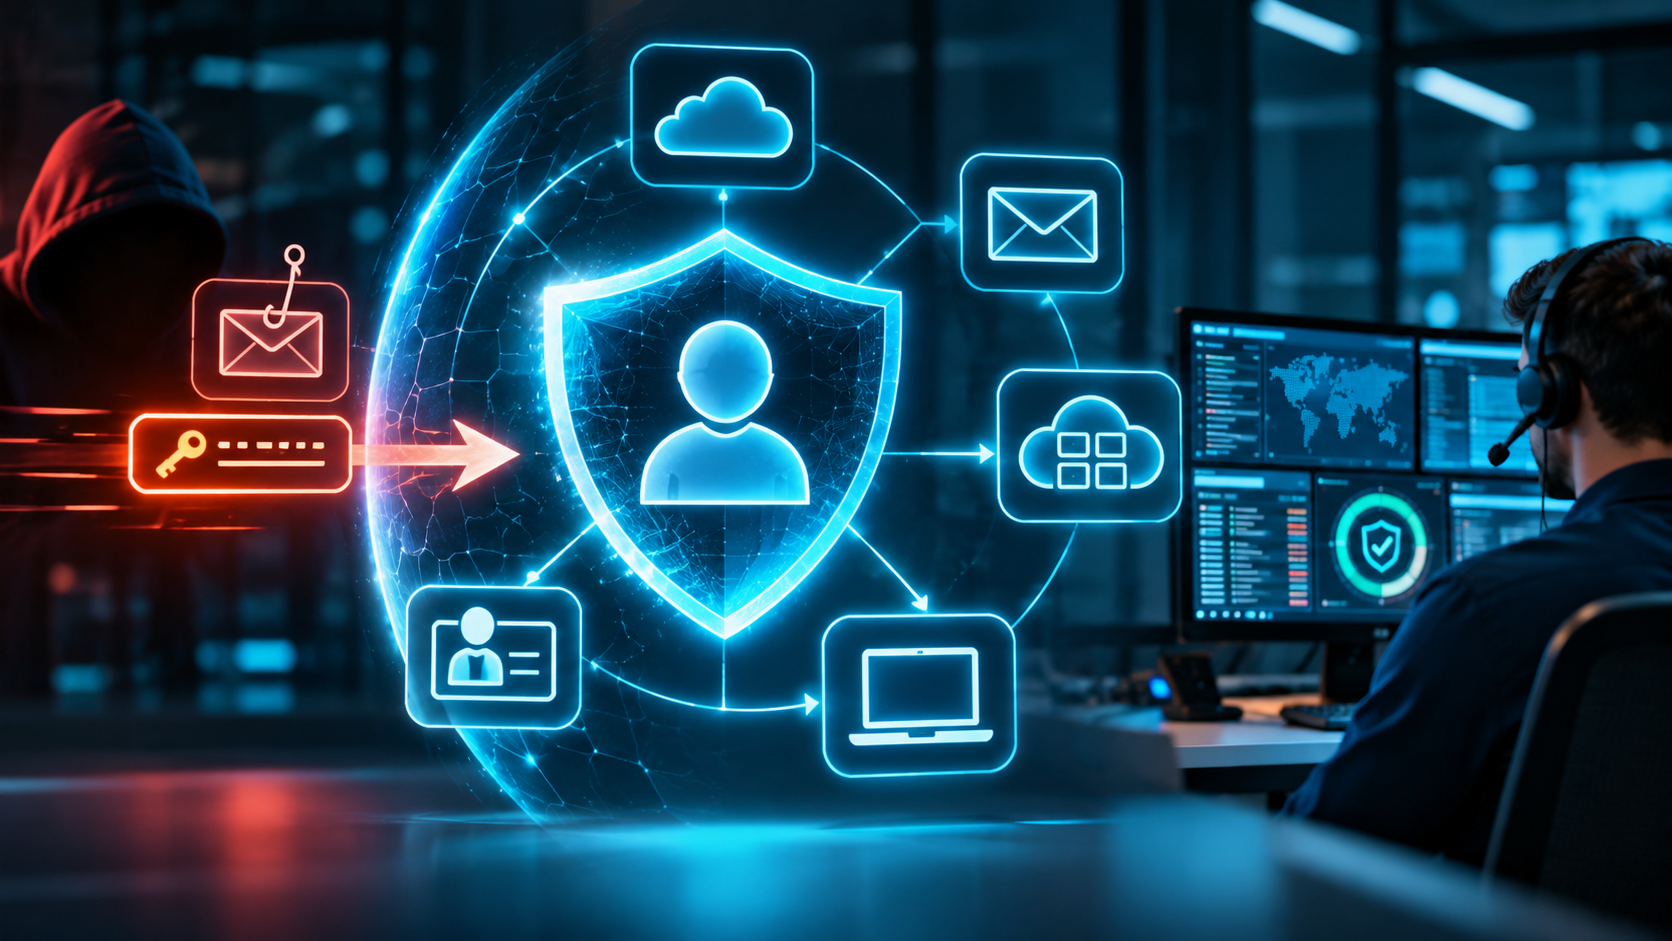
The attackers used adversary-in-the-middle (AiTM) phishing to capture session tokens after victims had completed multi-factor authentication, then replayed those tokens to access accounts without a password or a further MFA prompt. Once inside, they registered rogue devices and authenticator apps and set up inbox rules to hide their activity. In one case, a hijacked mailbox was used to send a payroll-related email to an external accountant.

Huntress Managed ITDR detected the activity first, and Microsoft Entra ID Protection flagged the same attacker infrastructure. Huntress says the campaign prompted it to rebuild its detection pipeline so that a single incident naming several accounts is attached to each affected identity.

The identity angle is central to the update. Huntress reports that in a recent two-week period, 85% of medium- and high-severity Defender incidents it saw carried no device-related evidence at all, meaning endpoint-centric tooling would have missed them.

Under the expanded integration, Huntress now ingests incident data from:

  • Microsoft Defender for Identity
  • Microsoft Defender for Office 365 (for example, phishing emails caught at the gateway)
  • Microsoft Defender for Cloud Apps (for example, risky OAuth applications)
  • Microsoft Entra ID Protection (for example, compromised-account verdicts)

Huntress analysts correlate these signals, prioritise the queue, confirm whether a threat is active and respond, before sending customers a report on what happened and what action was taken. Incidents are attached to the endpoints involved, the identities named, or both.

Analysts can also run advanced hunting queries against a customer’s own Microsoft tenant data, going back up to 30 days, to trace process trees, look for the same tooling on other devices, or review what an account did after a suspicious sign-in. Huntress applies its own per-tenant query limits so that its hunting does not exhaust the Microsoft API quota shared with other security tools.

“Attackers don’t care how big a company is, and neither should the quality of its defence,” said Adam Bates, Vice President of Product Management at Huntress. Bates added that Huntress integrates with the Defender Suite because organisations of every size need defence in depth, and that Defender signal helped uncover the token-replay campaign.

The capability is aimed at organisations licensed for Microsoft 365 E5 or Defender Suite for Business Premium that want round-the-clock response without building in-house capacity to triage Defender alerts. Existing customers whose Microsoft tenant and Defender for Endpoint are already connected to Huntress receive the expanded data automatically.

Huntress also highlighted a new Adversary Infrastructure capability within Managed ITDR, which converts one organisation’s incident into a same-day Conditional Access block across eligible, opted-in Entra ID P1 tenants.

ShareTweet
Previous Post

Keeper Security Launches Global Emergency Breach Response Service for Organisations Under Cyberattack

Recent News

Token-replay campaign hijacks 97 Microsoft 365 accounts as Huntress extends SOC response across Defender

Token-replay campaign hijacks 97 Microsoft 365 accounts as Huntress extends SOC response across Defender

November 18, 2026
Keeper Security Launches Global Emergency Breach Response Service for Organisations Under Cyberattack

Keeper Security Launches Global Emergency Breach Response Service for Organisations Under Cyberattack

November 18, 2026
6 Cybersecurity Lessons We Can Learn from the Biggest Data Breaches

6 Cybersecurity Lessons We Can Learn from the Biggest Data Breaches

November 18, 2026
Filigran’s OpenCTI Surpasses 400 Integrations

Filigran’s OpenCTI Surpasses 400 Integrations

November 18, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2027
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol