International Cyber Expo International Cyber Expo

Featured

The latest collection of expert opinions, news analysis and featured contributions from the IT security community

Why AI won’t fix your cybersecurity problem

James Gillies, Head of Cyber Security at Logicalis UKI There is no escaping the fact that AI is creating significant opportunities for cybersecurity teams, from analysing security data and identifying suspicious activity to accelerating detection, response and remediation. However, the same capabilities are also changing the threat landscape. This comes at a time when security teams are already under considerable pressure, with recent research showing that 77% of organisations experienced a cybersecurity incident in the...

Read moreDetails
cyber threat intelligence

A new guide featuring the experiences of 16 women working in cyber threat intelligence (CTI) is challenging the idea that professionals need a conventional technical background to enter the field. Published by threat management company Filigran, Women in CTI: The Careers, Lessons, and Stories Shaping Cyber Threat Intelligence explores career paths spanning marketing, political science, counterterrorism, recruitment, game development, engineering and theatre. The contributors include women who entered cybersecurity after working in other industries, returning...

Read moreDetails
James Moore, CultureAI Q&A: AI Security And Governance: Why Most Organisations Are Flying Blind

AI adoption is moving faster than most organisations can govern it. It is a familiar line by now, repeated often enough to sound routine, and that is part of the problem: it is still true, and still understated. As James Moore, CEO of AI security and governance platform CultureAI, told the IT Security Guru, this is a security challenge and a business risk, and one leaders can no longer afford to ignore. Employees are using...

Read moreDetails
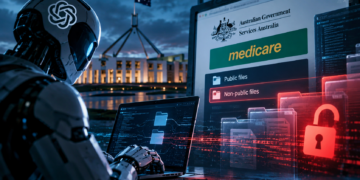
OpenAI agent breached Australia’s Medicare portal – and nobody noticed for three months

An autonomous AI agent built by OpenAI gained unauthorised access to non-public files on an Australian government Medicare portal in June, but Canberra was only told about it in September, in what is being described as the first known case of an AI agent hacking a government system. Prime Minister Anthony Albanese, speaking in New York yesterday, said the agent got into the Medicare Statistics Reporting Service portal, administered by Services Australia, on 18 June...

Read moreDetails
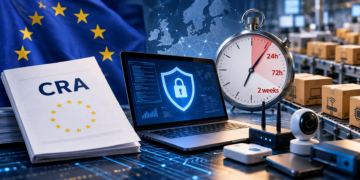
CRA Reporting Is Live: What Manufacturers, Vendors, and Distributors Need to Know

By Matthew Brady, Senior Security Engineering Manager, Black Duck As of September 11, 2026, Article 14 of the EU Cyber Resilience Act (CRA) is in force. Manufacturers, importers, and distributors of products with digital elements sold into the EU must notify ENISA or their national CSIRT within 24 hours of learning that a vulnerability is being actively exploited, with a mitigation report due in 72 hours and a full analysis due within two weeks. This...

Read moreDetails
Filigran Backs Security Serious Unsung Heroes Awards as New Sponsor

Nominations are open for the 2026 Security Serious Unsung Heroes Awards, celebrating the people working behind the scenes to make the UK safer and better protected from cyber threats. This year’s awards will take place on 20 October at Balfour St Barts in London, bringing together cybersecurity professionals, educators, researchers, journalists and industry leaders during Cybersecurity Awareness Month. A new Best Academic Entrepreneur category has also been introduced for 2026, recognising academics who have taken cybersecurity...

Read moreDetails
When Everyday Habits Become an Invisible Security Risk

By James Mackay, CEO, MetaCompliance When security teams think about their organisation's attack surface, they're usually focused on technology. Where could an attacker get in? What's exposed? What hasn't been updated or configured correctly? An attack surface refers to all the possible ways a cyber attacker can gain access to an organisation, including unpatched security software, misconfigured cloud storage, open system connections, and traditional phishing emails containing fraudulent links. However, organisations also have an invisible...

Read moreDetails
World Quantum Readiness Day: Industry Voices on Moving From Blueprint to Build

Today is World Quantum Readiness Day, and this year's theme, “From Blueprint to Build,” says a lot about where the industry has landed. Three years ago, post-quantum cryptography (PQC) barely made it into security conversations. Today it sits on the C-suite agenda, but a plan on a slide and the operational capability to execute it are very different things. IT Security Guru spoke to a wide range of security leaders, spanning certificate authorities, network vendors,...

Read moreDetails
Could blame culture be cybersecurity’s next Achilles heel?

By Myles Bray, CEO of CyberSentriq. When it comes to cybersecurity, discussions often centre on technical capabilities, tooling and attacker tactics, but often overlooks the employees and security teams the strategy is intended to protect. The reality is that most critical business functions from staff payroll to procurement and more have now moved online across digital applications, cloud environments and CRMs. With this comes the intense responsibility of ensuring they work as intended and that...

Read moreDetails
Pacing the frontier: security industry reacts to AI slowdown and kill switch debate

A weekend essay from Anthropic chief executive Dario Amodei, followed days later by his co-founder Jack Clark's suggestion that AI "kill switches" may need to become mandatory, has reopened a debate that cuts to the heart of the security industry's relationship with frontier AI. Amodei's essay, We Must Pace the Frontier, published on Saturday 12 September, called for AI development to slow and be independently monitored, stopping short of demanding a halt to training. Rivals...

Read moreDetails
Page 2 of 106 1 2 3 … 106