International Cyber Expo International Cyber Expo
  • About Us
Monday, 28 September, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

Scammers Exploit Shopify’s Own Notification System in New ‘Fake Refund’ Scam

by Guru Writer
August 13, 2026
in Featured
Scammers Exploit Shopify’s Own Notification System in New ‘Fake Refund’ Scam
Share on FacebookShare on Twitter

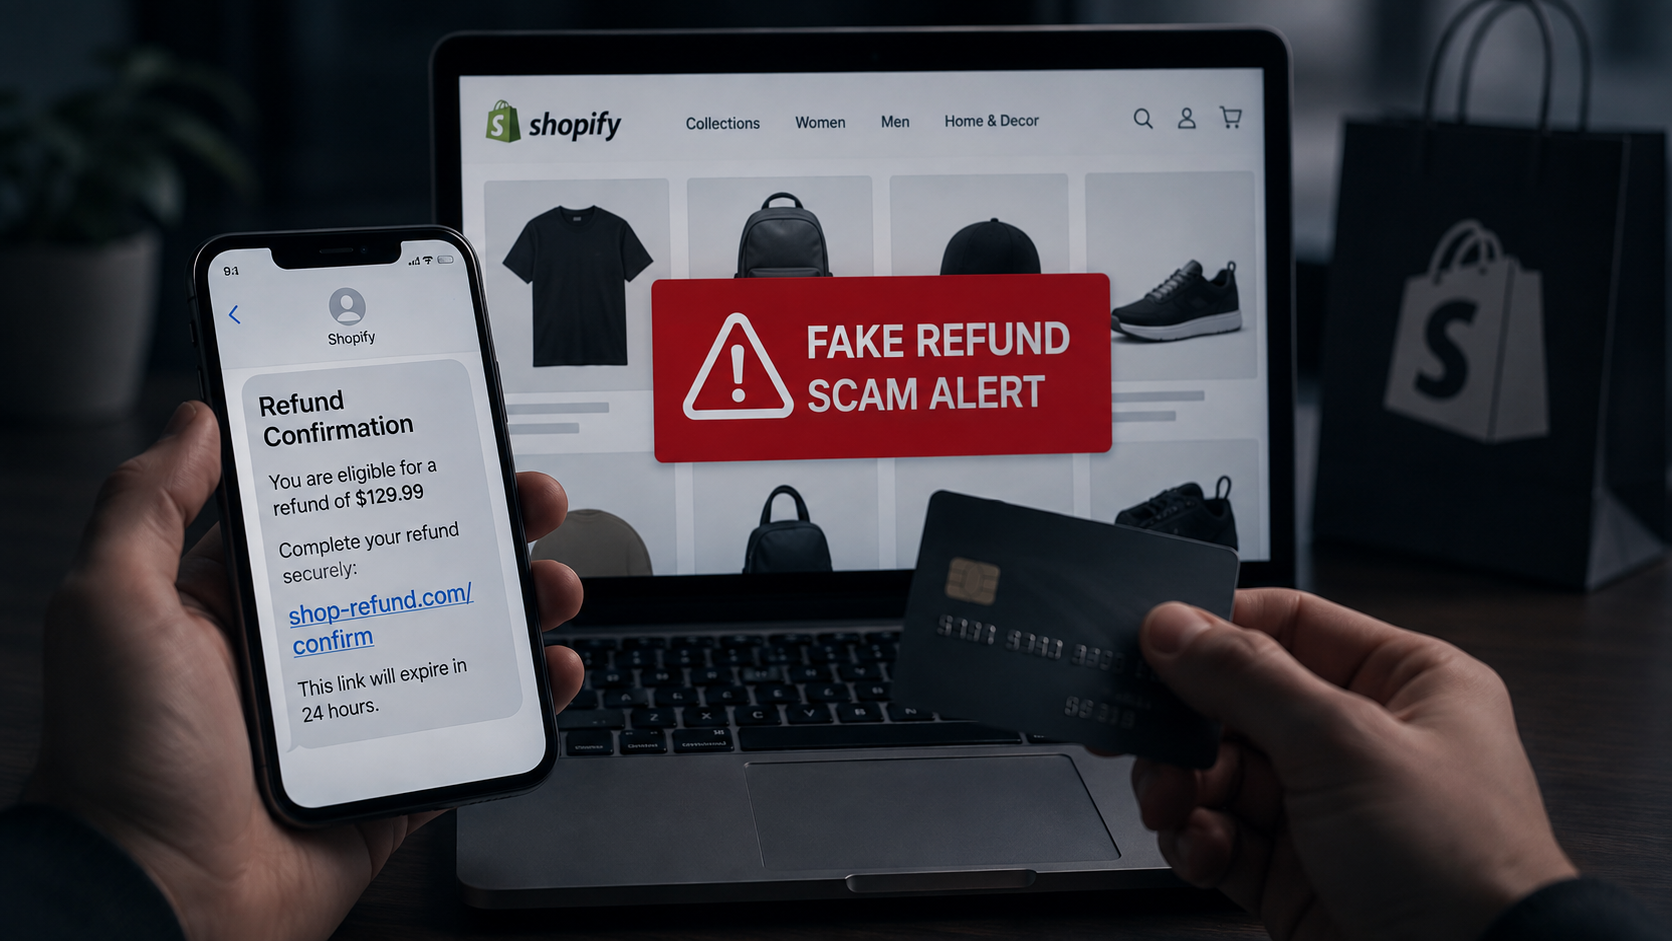
Security researchers have identified a phishing campaign that abuses Shopify’s own Shop app to deliver fake order and refund notifications directly to victims’ phones, marking a notable evolution of the classic “fake refund” scam.

According to research from cybersecurity firm Huntress, attackers are creating fraudulent Shopify seller accounts, or hijacking legitimate ones, to generate bogus orders against victims’ phone numbers or email addresses. Because Shopify’s Shop app treats these as genuine transactions, targets receive real push notifications and in-app receipts, rather than a suspicious email or text from an unfamiliar sender. Huntress said several of its own employees were targeted between May and August 2026, and that the technique has also been documented by researchers at Gen Digital and reported by users on Reddit.

In one example cited by Huntress, a fake receipt dated 7 August billed the recipient $339.96 for a “premium PC protection plan,” complete with a fabricated invoice number and transaction ID. The real sting sits in the shipping address field, which attackers repurpose to display a message urging the recipient to call a phone number if they did not place the order. Some variants dispense with the fake address altogether and instead push recipients toward the number via the order description, while others add a spoofed “out for delivery” shipment tracker to increase pressure on the target.

Victims who call the number are funnelled into a standard refund scam. Huntress said callers are typically talked into installing remote access tools such as ScreenConnect or AnyDesk, or into logging into their online banking. From there, scammers manipulate on-screen figures, sometimes editing displayed transaction details or coaching victims to misread a refund amount, to convince them they were mistakenly overpaid. Victims are then pressured to “return” the difference, usually by purchasing gift cards and handing over the redemption codes, which attackers cash out quickly.

Huntress frames the campaign as a variant of a technique it calls Living off Trusted Sites (LoTS), where attackers route victims through a legitimate, trusted platform before reaching a malicious outcome, rather than relying on a fake domain that is easier to flag. While earlier LoTS attacks used links to services such as Dropbox, Canva, or DocuSign to add credibility, this campaign instead abuses Shopify’s own notification pipeline to generate content that looks and functions exactly like a native alert. The firm noted a similar pattern in a previous campaign involving genuine PayPal invoices carrying fraudulent callback numbers.

Shopify has acknowledged the scam in its Help Center. The company and Huntress both advise users not to interact with unfamiliar phone numbers, email addresses, or links found within an order, and to contact Shop Support directly if they are concerned about the security of their account. Users who receive a suspicious order notification are advised to check their bank statements before assuming any charge went through, and can flag the order as “Not my order” within the Shop app. Huntress also recommends checking a store’s reviews and history before purchasing, noting that many of the fraudulent shopfronts used in this campaign were newly created.

ShareTweet
Previous Post

Akira Ransomware Affiliate Rebooted Into Safe Mode to Dodge EDR and Broke Its Own Attack

Next Post

Meet Huntress at International Cyber Expo 2026

Recent News

cyber threat intelligence

New Guide from Filigran Highlights the Many Routes Women Take into Cyber Threat Intelligence

September 28, 2026
James Moore, CultureAI Q&A: AI Security And Governance: Why Most Organisations Are Flying Blind

James Moore, CultureAI Q&A: AI Security And Governance: Why Most Organisations Are Flying Blind

September 28, 2026
Attackers build “silent” cryptominer on victim’s machine and give themselves away

Attackers build “silent” cryptominer on victim’s machine and give themselves away

September 25, 2026
OpenAI agent breached Australia’s Medicare portal – and nobody noticed for three months

OpenAI agent breached Australia’s Medicare portal – and nobody noticed for three months

September 25, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol