International Cyber Expo International Cyber Expo
  • About Us
Thursday, 8 October, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

No EDR, no problem: how Huntress rebuilt an Akira ransomware attack from forensic leftovers

by Guru Writer
October 8, 2026
in News
No EDR, no problem: how Huntress rebuilt an Akira ransomware attack from forensic leftovers
Share on FacebookShare on Twitter

Incident responders rarely get to watch an attack from the beginning. More often, security tooling arrives after the damage is done, either as part of the response or because a rollout was still underway when the attackers struck. That was the position Huntress found itself in this September, when its agent was deployed at an organisation that had already been hit by Akira ransomware.

A post-compromise install means the EDR telemetry that would normally show initial access, reconnaissance, credential theft and persistence simply doesn’t exist. In a new write-up, Huntress researcher Harlan Carvey and colleagues show that missing data streams are not the same as missing evidence.

The tip of the iceberg

The first sign of trouble came shortly after the agent went live. An EDR signal fired on a domain controller, showing an executable named svchost.exe running under the SYSTEM account from C:\PerfLogs\Temp\ and loading a file called config.dll. It turned out to be a GOST (Go Simple Tunnel) binary, an open-source proxy and tunnelling tool that has previously been linked to Akira affiliate activity.

Everything that came before had to be reconstructed from what was left on disk: Windows Event Logs, Registry artefacts and log files written by the ransomware itself.

Reconstructing the kill chain

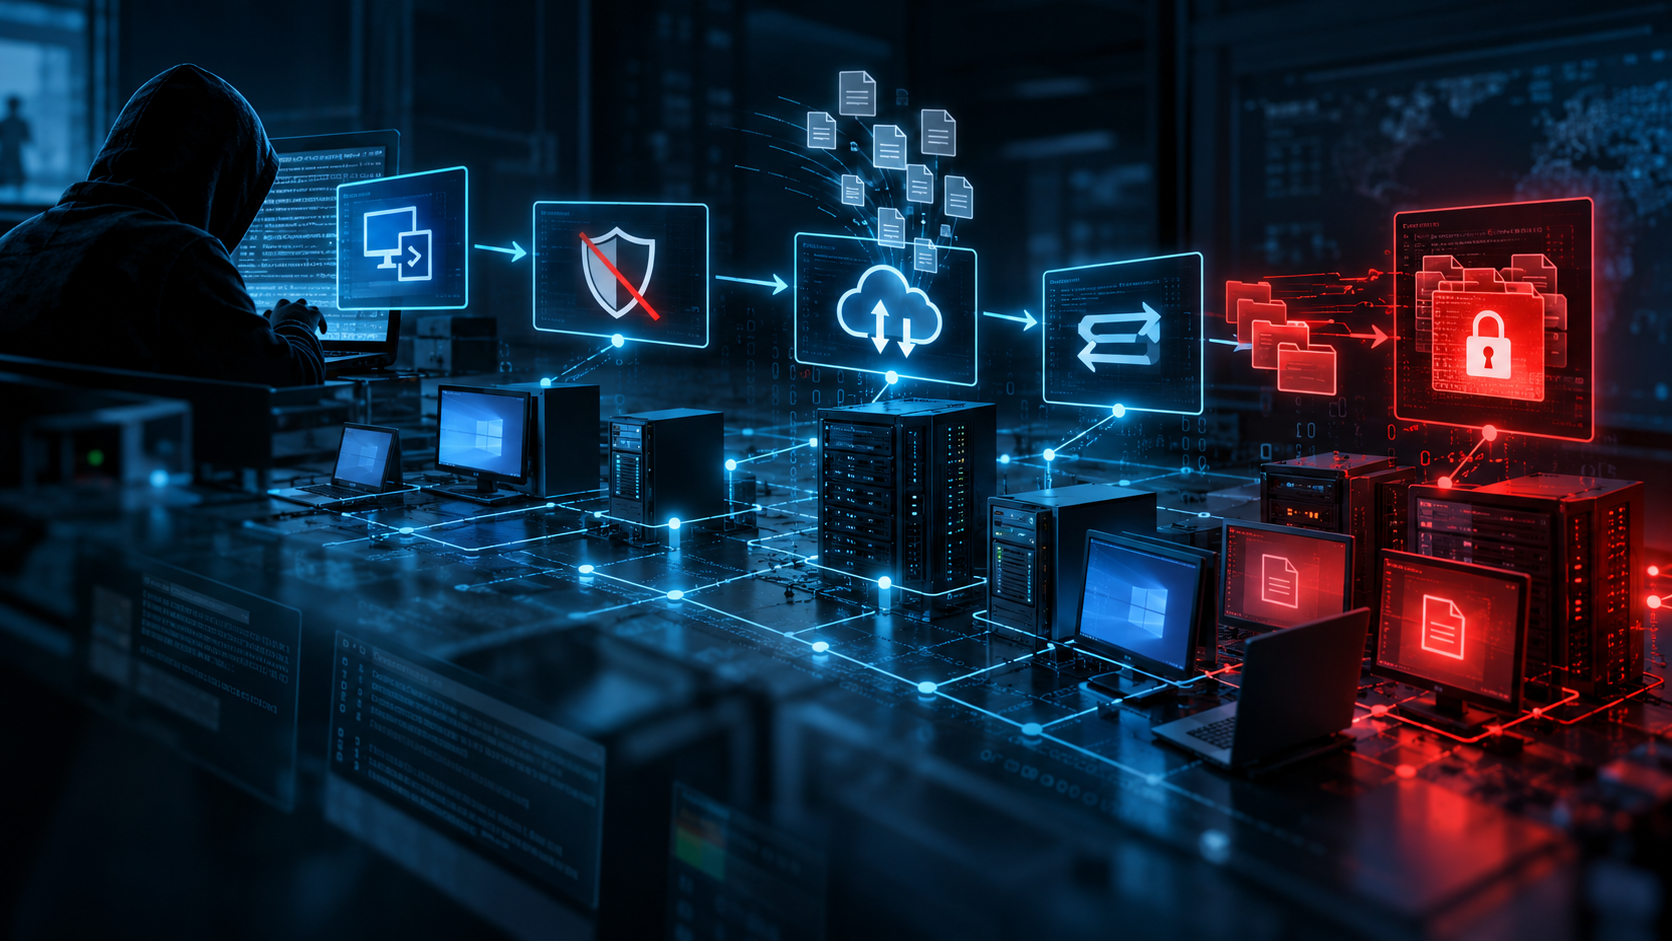
Event logs showed the attacker connecting over RDP from a workstation that did not belong to the victim (hostname C1IFRYXI). Shortly afterwards, the Bitdefender console was accessed and four Bitdefender services were stopped, with Service Control Manager event 7036 recording each one.

From there, the timeline follows a familiar pattern:

  • Credential access: exe was run from C:\PerfLogs, most likely to dump LSASS memory.
  • Persistence: the GOST tunnel was deployed, communicating with 64.227.4[.]134.
  • Exfiltration: Rclone was launched from the same folder, a tool Huntress has repeatedly seen used to sync stolen data to cloud storage.
  • Impact: Akira was run against the organisation’s file shares.
Toolmarks instead of command lines

Without process telemetry, there was no recorded ransomware command line. Instead, the researchers relied on what they describe as toolmarks: the distinctive side effects a tool leaves behind simply by doing its job.

Shellbags showed the attacker browsing subfolders under a Shares directory. At the same moment, the PowerShell event log captured a command deleting volume shadow copies via Get-WmiObject Win32_Shadowcopy, a standard Akira move to block recovery. An Akira log file was created at the same time, confirming the ransomware had targeted that folder.

Less than a minute later, Shellbags showed the attacker opening one of the encrypted subfolders in Windows Explorer, apparently to check the encryption had taken. The same sequence of launch, shadow copy deletion, log file and visual check repeated three more times. Around four hours after encryption began, the GOST tunnel was set up to keep a way back in.

What defenders should take away

Huntress’s recommendations are deliberately practical:

  • Keep an accurate inventory of physical and virtual systems and applications.
  • Reduce the attack surface so there is less to monitor and maintain.
  • Enforce MFA on any remote access that has to be exposed.
  • Alert on logons from unknown or suspicious workstations.
  • Watch locations such as C:\PerfLogs for new executables being created and launched.

The full analysis, including indicators of compromise and file hashes for the Akira payload and the GOST binary, is available on the Huntress blog.

ShareTweet
Previous Post

When everything looks normal: why context, not more alerts, is the next frontier for security operations

Next Post

Digital IDs and the AI threat: verification must evolve, not just digitise

Recent News

Marc de Beaucorps, Co-founder and CEO of Finovox

Digital IDs and the AI threat: verification must evolve, not just digitise

October 8, 2026
No EDR, no problem: how Huntress rebuilt an Akira ransomware attack from forensic leftovers

No EDR, no problem: how Huntress rebuilt an Akira ransomware attack from forensic leftovers

October 8, 2026
When everything looks normal: why context, not more alerts, is the next frontier for security operations

When everything looks normal: why context, not more alerts, is the next frontier for security operations

October 8, 2026
Tines Named Headline Sponsor of CSIDES 2026 in Weston-super-Mare

Tines Named Headline Sponsor of CSIDES 2026 in Weston-super-Mare

October 8, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol