International Cyber Expo International Cyber Expo
  • About Us
Thursday, 8 October, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

When everything looks normal: why context, not more alerts, is the next frontier for security operations

by Lara Joseph
October 8, 2026
in Featured
When everything looks normal: why context, not more alerts, is the next frontier for security operations
Share on FacebookShare on Twitter

Security awareness has long relied on teaching people to spot the obvious warning signs. Steve Povolny, Vice President of AI Strategy & Security Research at Exabeam, says attackers have been studying the same lessons. “The security industry has spent years teaching people what suspicious looks like: bad grammar, strange links, logins from impossible locations. Attackers have been adapting to those lessons, too.”

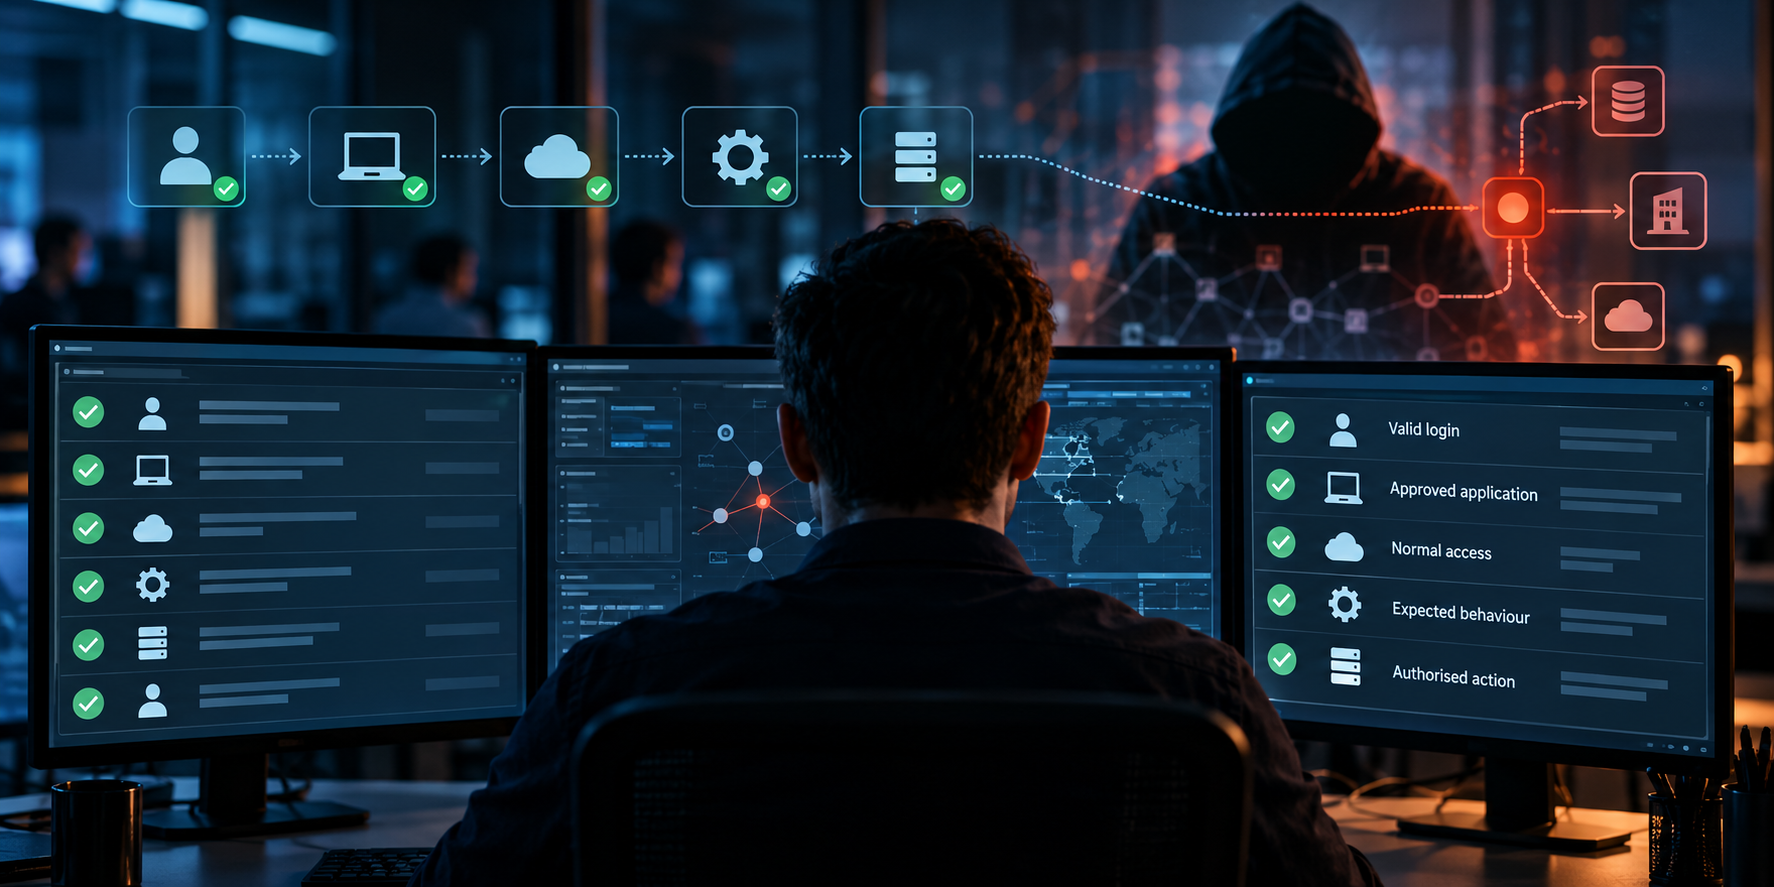
The result is a growing class of intrusions that look entirely legitimate on the surface. “A stolen session token can authenticate normally. A compromised employee can use applications they’re supposed to use. A North Korean IT worker can enter through the hiring process rather than an exploit chain,” Povolny explains. “An AI agent can take authorized actions and still produce an outcome nobody intended.”

At the same time, security operations centers are hardly short of data. “The modern SOC doesn’t have an information problem. It has a decision problem,” says Nick Tausek, Lead Security Automation Architect at Swimlane. “Analysts already have alerts, threat intelligence, identity data and endpoint telemetry. The slowdown happens when someone has to figure out which signal deserves attention, what context is missing and what should happen next.”

Behavior over time

Povolny argues that detection must shift from single events to patterns. “That’s why individual events are less meaningful in isolation. Modern detection has to understand behavior over time,” he says. “What does this identity normally access? Which systems and applications does it use? How does today’s sequence compare with its behavior over the past several months?”

That has implications for what organizations can reasonably expect of their staff. “The signal may not be one dramatic action. It may be a series of legitimate actions that have never occurred together before,” Povolny says. “Employees can and should report an unusual request or interaction, but we can’t expect them to recognize a valid login, an approved tool or a sequence of routine actions that only becomes concerning in context.”

Which one gets fixed first?

Piyush Sharrma, co-founder and CEO at Tuskira, sees the same problem in vulnerability management, and poses a thought experiment. “Picture two vulnerabilities. One carries a critical severity score but sits on an isolated system with strong controls around it. The other looks far less dramatic. It happens to connect an exposed application to a privileged identity and then to production.”

“Which one gets fixed first?” he asks.

“For years, vulnerability management has made it too easy to answer that question with severity alone,” Sharrma says. “Attackers aren’t working from a sorted CVE list. They’re looking for combinations of weaknesses that get them somewhere useful.”

AI, he believes, can help defenders see the environment the way an attacker does. “AI-assisted attack-path analysis can trace those combinations across identity, cloud, network and application environments. It can show which weaknesses are actually reachable. It can also identify whether an existing control cuts off the path before an attacker reaches something valuable.”

Matching intelligence to the problem

Tausek cautions that AI in the SOC must justify its place, and that not every case warrants the same treatment. “The AI SOC needs to earn its keep. Not every incident needs the same level of intelligence,” he says. “Routine cases can move through deterministic automation. More ambiguous activity may need AI-assisted investigation. A smaller group of complex threats can justify fully agentic analysis. Human judgment stays focused on the decisions where experience matters most.”

Sharrma says the goal should be clarity rather than ever-larger numbers. “Organizations don’t need more awareness of how many vulnerabilities they have. Most already know the number is uncomfortable. They need a better understanding of which ones can become a breach.”

Tausek agrees that speed alone will not solve the problem. “Cybersecurity Awareness Month is a useful reminder that faster detection alone isn’t enough,” he says. “Security operations need a way to turn what they know into action without forcing analysts to manually rebuild context every time something goes wrong.”

For Povolny, that is the core lesson for this year’s campaign. “Security programs and detection need to account for that ambiguity. Sometimes the credentials are valid, the tools are approved, and each action looks normal,” he concludes. “Behavioral context is what gives security teams a chance to see when those normal-looking pieces stop adding up.”

ShareTweet
Previous Post

Tines Named Headline Sponsor of CSIDES 2026 in Weston-super-Mare

Next Post

No EDR, no problem: how Huntress rebuilt an Akira ransomware attack from forensic leftovers

Recent News

Marc de Beaucorps, Co-founder and CEO of Finovox

Digital IDs and the AI threat: verification must evolve, not just digitise

October 8, 2026
No EDR, no problem: how Huntress rebuilt an Akira ransomware attack from forensic leftovers

No EDR, no problem: how Huntress rebuilt an Akira ransomware attack from forensic leftovers

October 8, 2026
When everything looks normal: why context, not more alerts, is the next frontier for security operations

When everything looks normal: why context, not more alerts, is the next frontier for security operations

October 8, 2026
Tines Named Headline Sponsor of CSIDES 2026 in Weston-super-Mare

Tines Named Headline Sponsor of CSIDES 2026 in Weston-super-Mare

October 8, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol