International Cyber Expo International Cyber Expo
  • About Us
Tuesday, 13 October, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

LiteLLM flaws let low-privileged users hijack AI gateway and steal provider keys

by Guru Writer
October 13, 2026
in AI and Machine Learning, News
LiteLLM flaws let low-privileged users hijack AI gateway and steal provider keys
Share on FacebookShare on Twitter

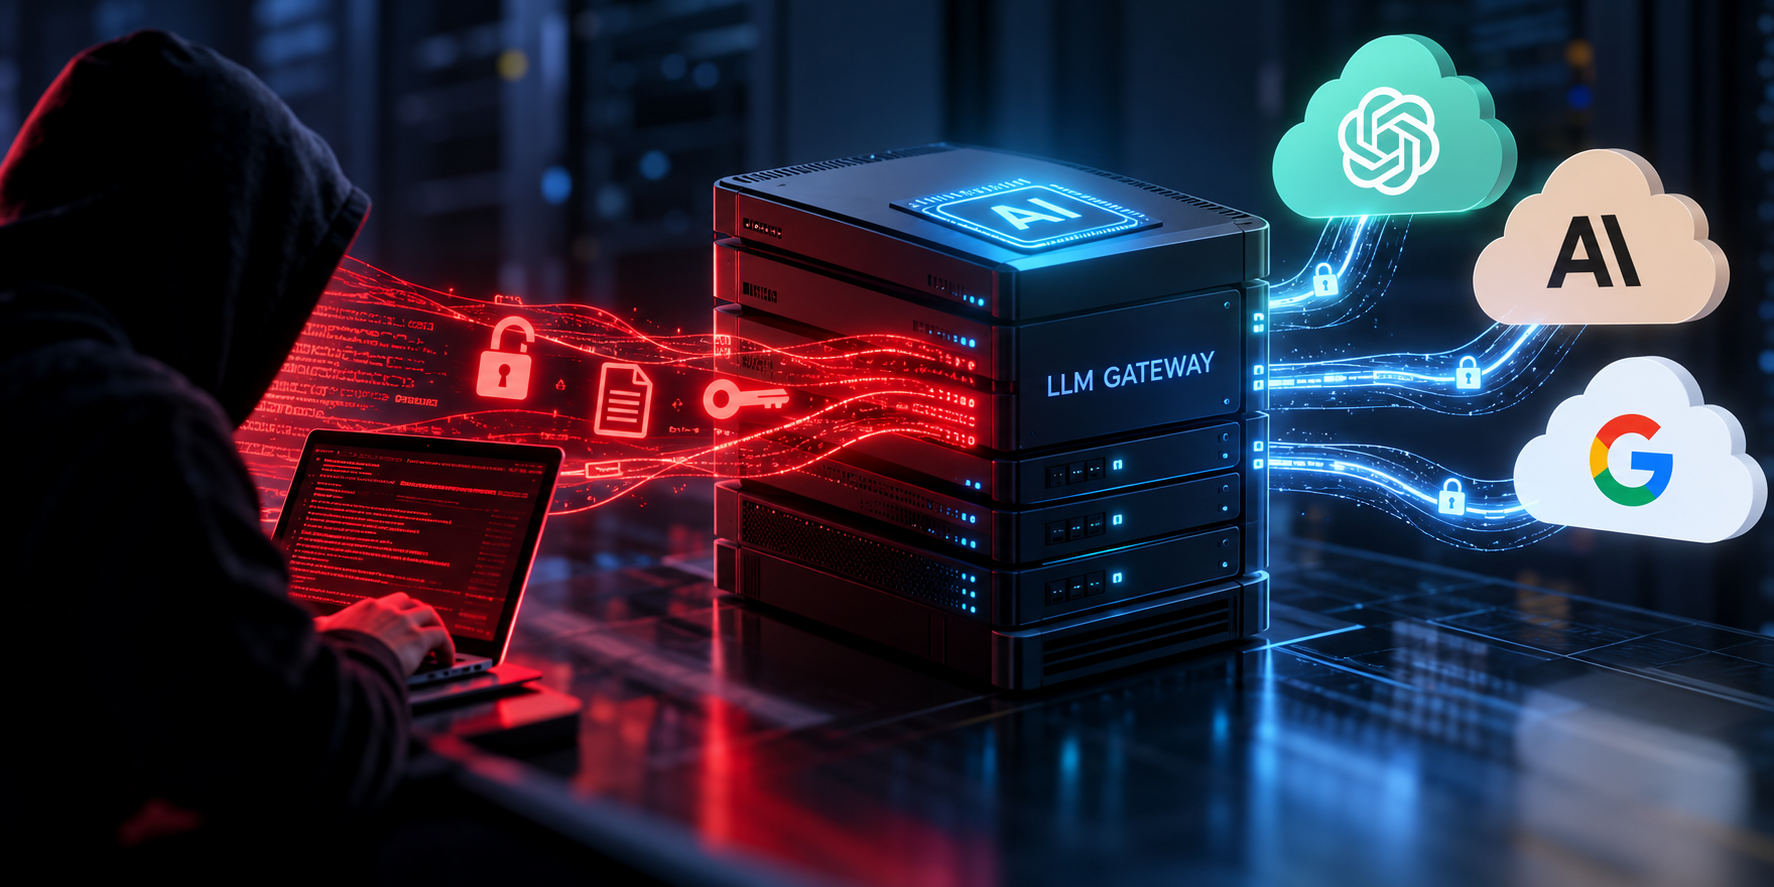
Check Point Research has disclosed two high-risk vulnerabilities in LiteLLM, the open-source gateway that sits between enterprise applications and AI providers such as OpenAI, Anthropic and Google. The flaws could allow a user with minimal privileges to take full control of the gateway, read sensitive files, execute arbitrary code and harvest the API keys an organisation uses to access its AI providers.

LiteLLM is downloaded around 97 million times a month and has more than 59,000 stars on GitHub. Both issues, tracked as CVE-2026-35029 and CVE-2026-59823, are fixed in version 1.83.9.

One endpoint, three attack paths

The more serious flaw, CVE-2026-35029, is a missing authorisation check on LiteLLM’s /config/update endpoint, which controls the proxy’s runtime configuration. Unlike other administrative endpoints, it did not verify that the caller held the PROXY_ADMIN role.

Compounding this, any user who logs in through the LiteLLM dashboard is issued a session token tied to a special “litellm-dashboard” team, and those tokens are checked against a looser list of permitted UI routes. That list includes “/config”. Because the check uses simple prefix matching, requests to /config/update were allowed for any logged-in user, whatever their role.

Testing against LiteLLM version 1.77.7, the researchers showed the flaw could be used to:

  • Read arbitrary files, by injecting an environment variable that sets the path of the dashboard logo and pointing it at sensitive files such as /etc/passwd
  • Take over the built-in admin account, by overwriting the UI_USERNAME and UI_PASSWORD variables and logging in with attacker-chosen credentials
  • Execute remote code, by registering a “pass-through endpoint” that loads a Python module from an attacker-controlled S3 or GCS bucket, which LiteLLM then downloads and runs
Stealing keys without touching the provider

The second flaw, CVE-2026-59823, is a server-side request forgery (SSRF) issue in LiteLLM’s “Clientside LLM Credentials” feature. By passing a user_config parameter to the /chat/completions endpoint, an authenticated user could create a router pointing at their own server. Requests, along with the provider API keys attached to them, would then be sent to the attacker rather than to the AI provider.

Check Point notes that this code path sidestepped restrictions LiteLLM already placed on client-supplied api_base and api_key parameters.

The researchers also found that password hashes were exposed to low-privileged users and were stored without salting, using a single hash iteration. These issues duplicated an existing advisory, GHSA-69×8-hrgq-fjj8.

Old bugs, bigger blast radius

Check Point is clear that none of these are new classes of “AI” vulnerability. Missing authorisation checks, SSRF and unsafe dynamic module loading are all well understood. What raises the stakes is where they sit. An LLM gateway stores provider keys, manages user permissions and routes every prompt and response, making it a single point of compromise for an organisation’s AI estate. And because LiteLLM is embedded in many other AI platforms and internal tools, some organisations may be running it without realising.

“The industry’s focus has largely been on securing AI models, but this research highlights an equally important reality: AI infrastructure is becoming a new critical layer of enterprise security,” said Mateo Rojas-Carulla, Head of Research, AI Agent Security at Check Point Software Technologies. “As organisations increasingly rely on gateways such as LiteLLM to connect applications, users and AI services, these platforms become attractive targets because they sit at the centre of trust.”

“For LiteLLM users, the immediate priority is patching and reviewing access controls, but the broader lesson extends beyond a single product,” he added. “Attackers will naturally target the layer that gives them the greatest access with the least resistance.”

What defenders should do

Check Point recommends that organisations:

  • Upgrade to LiteLLM 1.83.9 or later across every deployment, including instances embedded in other tools
  • Audit gateway user accounts and remove any that are not needed
  • Rotate AI provider API keys if there is any sign of unauthorised access before patching
  • Test that limited roles are enforced in practice, not just on paper
  • Bring LLM gateways into scope for regular security assessments

The vulnerabilities were reported to LiteLLM’s maintainers through a coordinated disclosure process that began in October 2025.

Full technical write-up: https://research.checkpoint.com/2026/when-llm-gateways-go-wrong-findings-from-litellm/

ShareTweet
Previous Post

Legacy refrigeration controllers exploited in OT attack on hundreds of French supermarkets

Recent News

LiteLLM flaws let low-privileged users hijack AI gateway and steal provider keys

LiteLLM flaws let low-privileged users hijack AI gateway and steal provider keys

October 13, 2026
Legacy refrigeration controllers exploited in OT attack on hundreds of French supermarkets

Legacy refrigeration controllers exploited in OT attack on hundreds of French supermarkets

October 13, 2026
Louise John, Head of IT Service Delivery at Virgin Active

Leading digital change when nobody prepared you for it

October 12, 2026
Lee Robson, AWS Greenfield Practice Lead at Ingram Micro

DTX + UCX 2026: Ingram Micro on Unlocking AI and Cloud Without Losing Control

October 12, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol