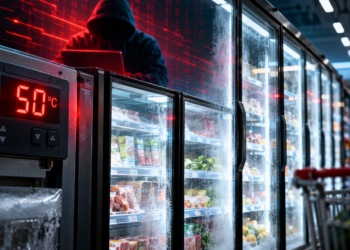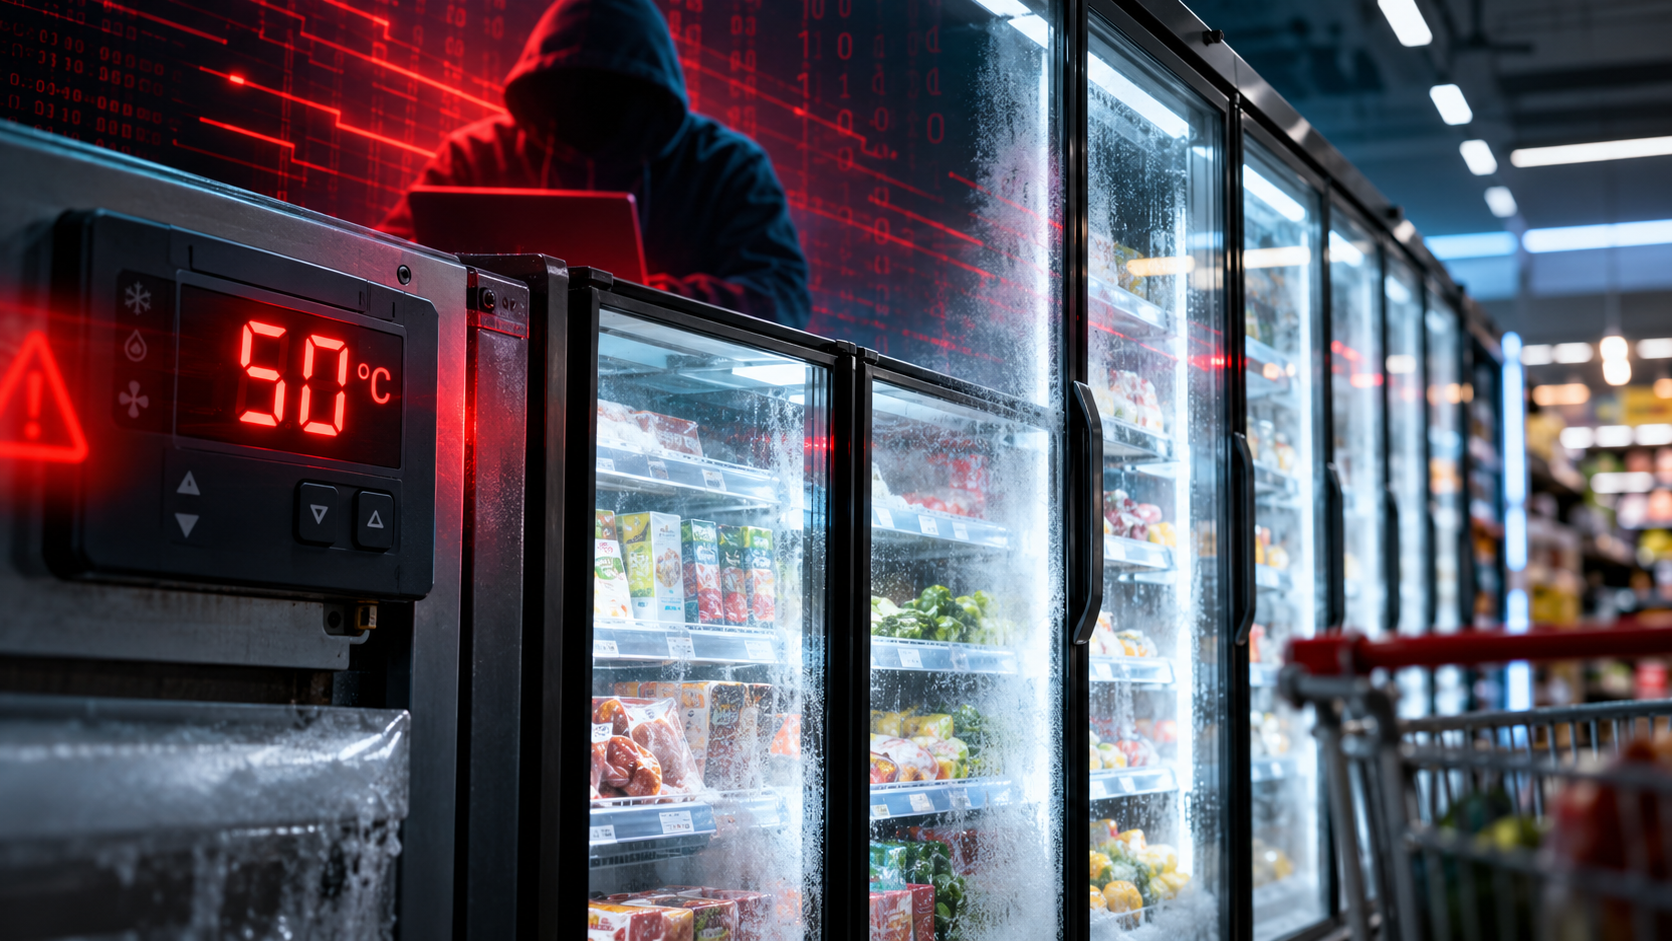
A coordinated attack on the operational technology (OT) behind supermarket refrigeration has hit hundreds of stores across France, in what security experts are calling one of the clearest examples yet of cyber sabotage with physical consequences.

Retailers confirmed the attack on Monday 12 October, with disruption reportedly beginning on Sunday night. Intermarché and its Netto brand said at least 300 shops were affected, Coopérative U more than 100 and Carrefour 80, with Monoprix, E.Leclerc and Auchan also reporting impacted stores. According to BFM TV, attackers remotely forced refrigeration units into continuous defrost cycles, driving temperatures up to 50°C. Paris prosecutors said the attack also caused fires.
“This incident is not surprising. A supermarket refrigerator is no longer just an electrical appliance. It is a computerized system connected to a network, enabling remote monitoring and control. While this connectivity allows refrigeration systems to be managed efficiently, it also exposes them to cyber security risks, particularly when operational equipment runs for years on outdated software, without regular security updates, and with management interfaces accessible from the internet,” said Oded Vanunu, Head of Vulnerability Research at Check Point.
Unpatched, internet-facing and end of life
The affected equipment has been traced to refrigeration management systems from Danish manufacturer Danfoss. A source close to Prime Minister Sébastien Lecornu said France’s National Cybersecurity Agency (ANSSI) had identified a vulnerability in Danfoss software, and the agency has been ordered to investigate.
Danfoss said most of the compromised units were “legacy” products that no longer receive software or security updates, singling out its AK-SM800 and AK-SC355 controllers, and noted that an affected version of the AK-SM800 was running outdated firmware. The company said it had long advised customers to upgrade or replace these models.
Known vulnerabilities in the control software date back to 2023, some rated critical, with patches available. In August, OT security firm Claroty published research describing flaws in Danfoss systems that could allow attackers to bypass authentication. Reports suggest attackers may have used the Shodan search engine to locate exposed devices, some of which are connected via 3G cards for remote monitoring.
“One of the significant aspects of this incident is that the attackers did not necessarily need sophisticated cyber capabilities. Refrigeration systems have legitimate operational functions, such as defrost cycles, and when an unauthorized party gains access to the system, those same functions can be exploited to disrupt operations. Unlike attacks aimed at stealing data or encrypting files, the impact here is on the physical operation of the equipment itself, with direct consequences such as food inventory losses and potential safety hazards.” Vanunu continued.
“In previous research conducted by Check Point on smart devices, including LG products, we demonstrated how a vulnerability in a centralised management platform could allow attackers to gain control of connected devices. However, in the current incident, it is still unclear exactly how the attackers gained access to the systems.”
OT in the crosshairs
No group has claimed responsibility, and there is no evidence of a ransom demand or data theft. The Paris prosecutor’s cybercrime unit has opened an investigation into what it described as a “large-scale” attack on connected refrigerators at several major food retailers, while ANSSI is coordinating with European counterparts. Sekoia analyst Felix Aime said stores in Spain, Portugal, Poland, Germany and Belgium were also affected.
“The refrigeration systems in supermarkets are operational technology. Building management controls, HVAC, cold chain infrastructure. These are the same category of systems that the security industry has been warning about as the next frontier for sabotage attacks, and they’ve now been weaponised against food retail infrastructure in one of Europe’s largest economies,” said Muhammad Yahya Patel, vCISO and cybersecurity advisor for EMEA at Huntress.
ANSSI had already listed sabotage of industrial control systems among the main threats facing France in its most recent threat report.
“Heating fridges to 50 degrees for six hours is not data theft; it is physical sabotage executed through software, and that is the lesson for every sector. Refrigeration controllers, building systems and point-of-sale equipment are now connected and remotely managed, often through a handful of suppliers, so one weak link scales to hundreds of stores overnight,” said Samuel Hassine, CEO and co-founder of Filigran.
“The problem extends beyond a single refrigeration system or an isolated security vulnerability. Operational equipment is often designed to remain in service for 15 years or more, while cyber threats and technologies evolve at a much faster pace. In addition, the same controllers and management systems are deployed across retail chains worldwide, meaning that a compromise affecting widely used technology could potentially impact a large number of locations,” added Check Point’s Vanunu.
Counting the cost
Intermarché chief executive Thierry Cotillard told BFM TV that losses could run to “tens of millions of euros nationwide in a single day”, while Coopérative U’s Dominique Schelcher said larger stores could each lose up to €180,000–200,000 in stock. France’s retail federation, the FCD, has called on Danfoss to provide “full transparency”.
“The immediate financial consequences are significant and visible. Failures at the stores means total write-off of perishable stock across every affected location simultaneously. The operational disruption compounds quickly. Staff cannot trade normally without functioning refrigeration. Products cannot be restocked until systems are restored and verified safe. The food retail sector across Europe should be treating this as a signal that they are being actively targeted,” Huntress’ Patel warned.
“The cyberattack on French supermarkets is a stark reminder that cyber threats extend far beyond stolen data and financial losses. Hackers reportedly manipulated refrigeration systems, raising temperatures to 50°C, causing fires and forcing retailers to dispose of large quantities of food. With hundreds of stores affected, the incident highlights how vulnerabilities in connected systems can have serious real-world consequences, disrupting operations, damaging equipment and potentially putting public safety at risk,” said Jamie Akhtar, CEO and Co-founder of CyberSmart.
Mitigation: find the exposure first
Experts agree that defenders’ first priority should be identifying which OT assets are reachable from the internet, and who holds remote access to them.
“To reduce these risks, the first step is to identify which controllers and management interfaces are directly exposed to the internet and eliminate any unnecessary exposure. It is also important to keep systems updated, replace default passwords, restrict remote access, and enable multi-factor authentication wherever supported. Separating operational control networks from other networks and monitoring unusual changes in system behaviour are also essential measures. These recommendations apply not only to refrigeration systems, but also to HVAC, building management systems, and other operational infrastructure.” said Vanunu.
“It also demonstrates how increasingly interconnected technology can create new opportunities for cybercriminals. For businesses, this reinforces the importance of securing all connected devices and systems, not just traditional IT infrastructure. Organisations should prioritise regular software and firmware updates, strong access controls, multi-factor authentication where supported and network segmentation to prevent attackers moving between systems. Regular security assessments and employee cybersecurity awareness training are also essential for identifying vulnerabilities before they can be exploited. Ultimately, businesses must recognise that cybersecurity is no longer just about protecting data, but also about safeguarding physical operations, customers and business continuity.” said CyberSmart’s Akhtar.
Filigran’s Hassine urged security leaders to put the issue in front of the board: “Boards should ask three questions this week. Which connected equipment could cause physical or financial damage if someone changed a setting, and who can reach it from outside. Which third parties hold remote access, and how that access is monitored and segmented. And has anyone tested that the response works, from detection to switching to manual operation. Resilience in retail now means knowing your exposure before an attacker maps it for you.”