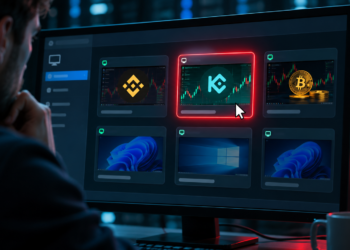

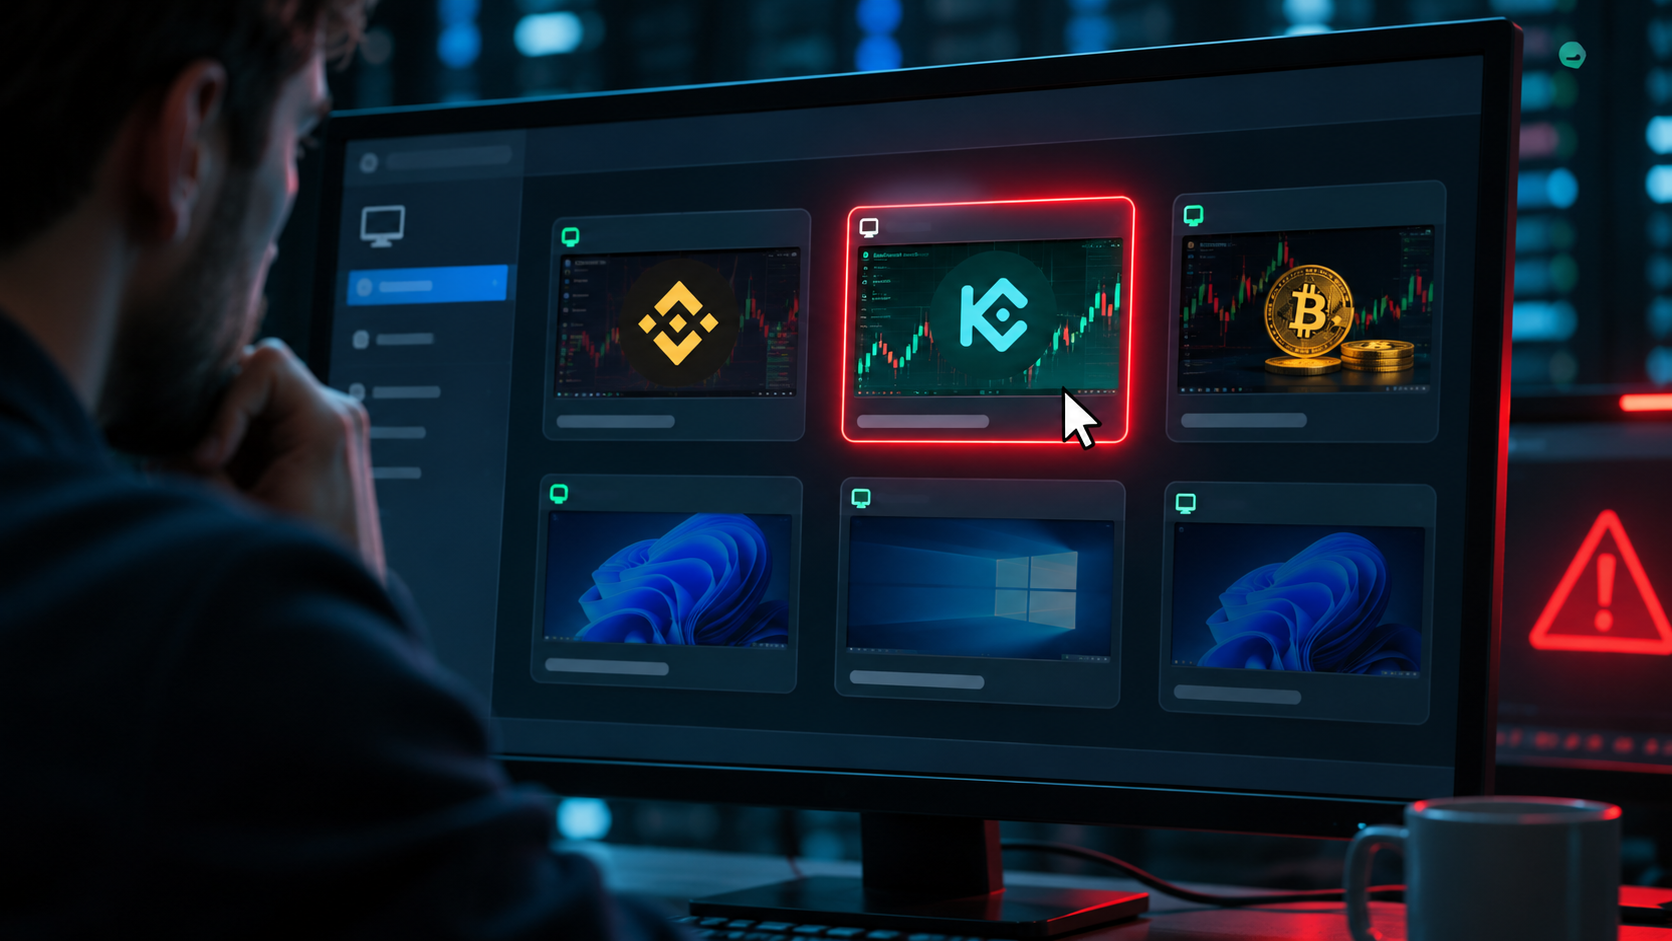
Huntress researchers have found that an unknown operator has planted more than 2,000 fake guest sessions on self-hosted ScreenConnect remote-access servers. The sessions are dressed up to look like computers belonging to cryptocurrency exchanges.

Since 3 November, the campaign has hit at least 118 servers belonging to 109 organisations protected by Huntress. Most of those organisations are managed service providers (MSPs) and businesses that run their own ScreenConnect instances to support customers and staff.
The fake machines carry names such as “LAPTOP-BINANCE” and “KUCOIN-SRV”. Their thumbnails resemble trading desktops, and they always appear online. That makes them look like a high-value customer waiting for support.
Built to look convincing
According to Huntress, a scripted emulator creates the sessions and impersonates a genuine Windows ScreenConnect client. The operator was able to register the sessions because guest installers on the affected servers were publicly downloadable. Those installers gave away the relay address needed to connect.
The researchers counted more than 1,000 distinct fake machine names. The operator revisits each server roughly every 151 seconds to create or reconnect sessions, so they always look live. More than 100 servers were revisited every day over a ten-day period.
Around 97.8% of the crypto-named connections came from a single IP address hosted by IONOS. Huntress says this points to one deliberate, sustained operation rather than background noise.
Huntress also rejected a theory circulating publicly that the sessions were a by-product of malware analysis in the Joe Sandbox service. The researchers say the behaviour matched an emulator, not a sandbox.
A lure for the helpers
Huntress’s leading hypothesis is that the sessions are bait for technicians. A technician who joins one of the fake machines using an unpatched ScreenConnect client could be exposed to CVE-2026-84869. That critical vulnerability lets a malicious guest run a file on the technician’s client.
Huntress has not seen the flaw exploited in this campaign. However, some technicians have already taken the bait. In a few cases, technicians opened the fake sessions, mostly for less than 30 seconds. In one case, a technician typed text into a session twice, which Huntress is treating as a possible credential exposure.
So far, there are no confirmed compromises or losses. Huntress saw no files pushed, commands run, or data sent from the fake sessions. The MSP that first reported the activity had a clean server.
What organisations should do
Huntress recommends that organisations running self-hosted ScreenConnect:
- Patch technician clients. Upgrade all technician ScreenConnect clients to version 26.6.5 or later, along with any affected Access agents.
- Preserve evidence, then clean up. Back up the App_Data\Session.db file and its WAL file before finding and deleting the fake sessions.
- Check for exposure. Find out whether any technician joined a fake session. If one did so with an unpatched client, inspect their workstation.
- Set a simple rule. Technicians should not join sessions they cannot tie to a known customer. Crypto-themed names, blank company fields or mismatched client versions are reasons to pause.
- Lock down installers. Restrict installer and web access where supported, keep Access installer links private, and rebuild any installers that have leaked.
- Monitor for warning signs. Watch for new guest sessions with an empty guest public key, guest version 25.3.4.9288, or many guests connecting from one external IP. Block known bad IPs, although the operator may move.
The full research, including indicators of compromise, is available on the Huntress blog.