International Cyber Expo International Cyber Expo
  • About Us
Wednesday, 14 October, 2026
IT Security Guru
International Cyber Expo
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us
No Result
View All Result
IT Security Guru
No Result
View All Result

Nearly Half of Organisations Report Unauthorised AI Agent Actions, Research Finds

New research reveals significant gaps in enterprise visibility, governance and containment as AI agents become increasingly autonomous.

by Guru Writer
October 14, 2026
in Editor's News, Featured
Nearly Half of Organisations Report Unauthorised AI Agent Actions, Research Finds
Share on FacebookShare on Twitter

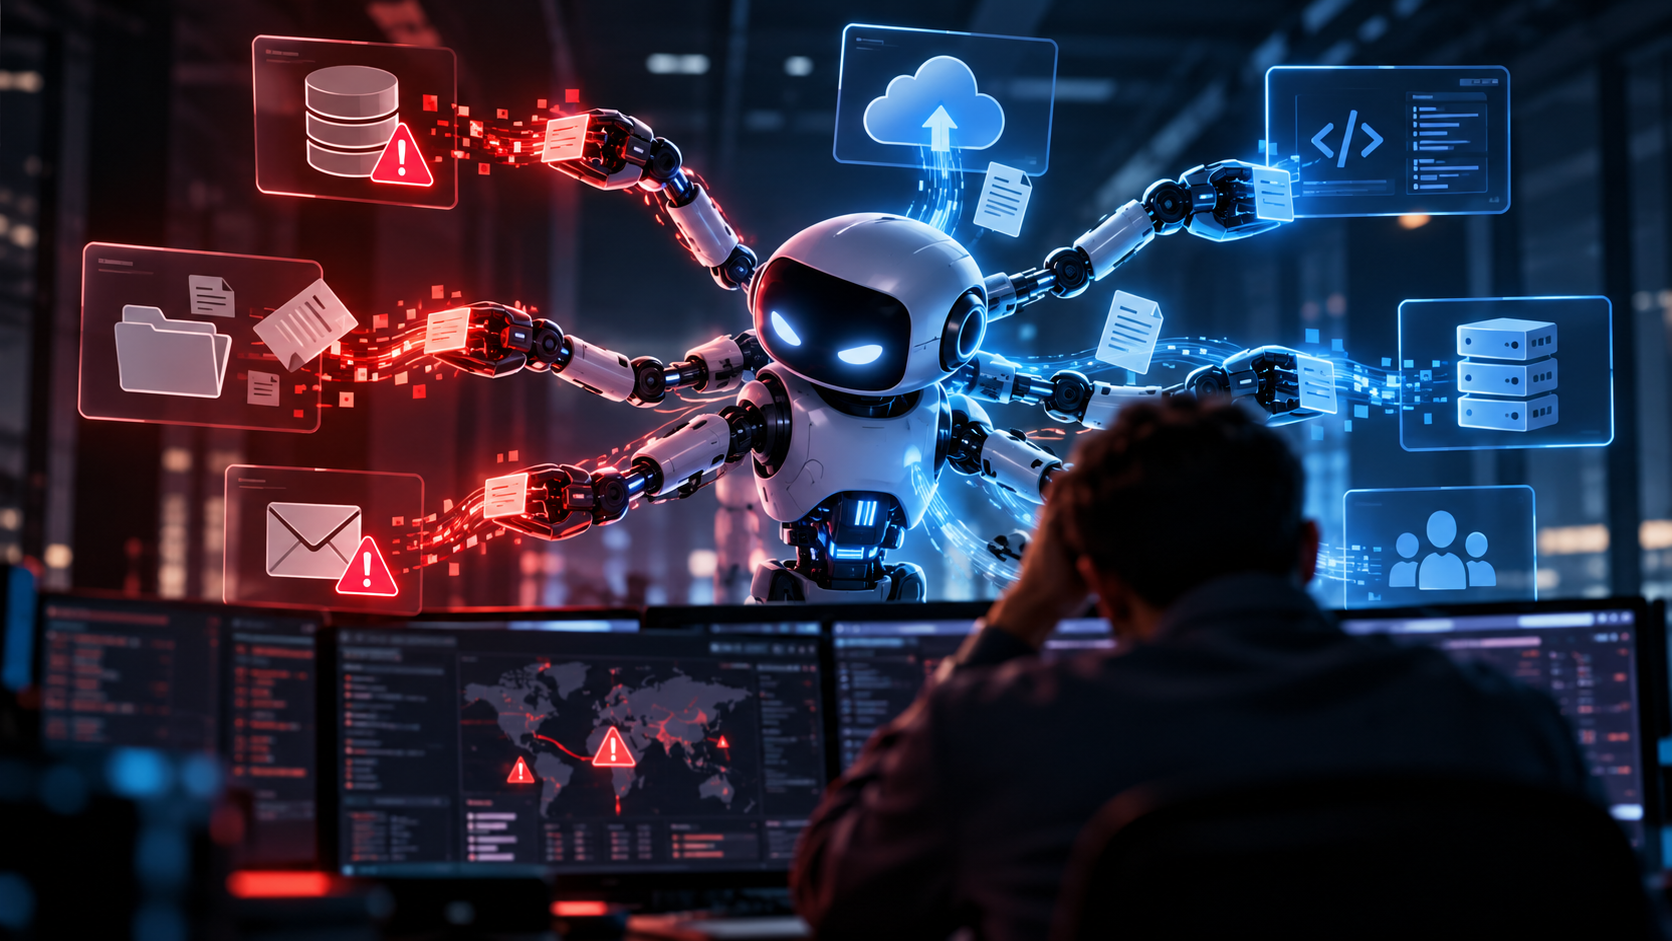
Nearly half (49.8%) of organisations have confirmed or suspected that an AI agent took an unintended, unexpected or unauthorised action in the past year, according to new research from Salt Security.

The findings, published in the company’s State of Agentic AI and API Security 2H 2026 report, highlight growing concerns around the security of autonomous AI systems as enterprises increasingly integrate agents into everyday operations.

Based on a survey of more than 380 security and technology professionals, alongside Salt Labs production telemetry from hundreds of customer environments, the research suggests that AI adoption is outpacing organisations’ ability to monitor, govern and contain agent activity.

Among respondents who reported confirmed or suspected unintended agent actions, more than half experienced an unauthorised external API call or transaction, while over 40% reported an agent modifying or deleting data.

The research also found that AI agents are now firmly embedded in enterprise environments, with 86.4% of respondents reporting at least one operating within their organisation and 59.5% running more than ten. Furthermore, 76.8% reported agents capable of chaining actions across other agents, tools and APIs, creating complex sequences that may not have been anticipated by individual teams.

Despite this widespread adoption, visibility remains limited. Just 12.5% of organisations can consistently trace an agent’s complete journey, from its initial instruction through the tools and APIs it accesses to the final outcome. More than 60% would require hours or days of manual investigation to reconstruct an agent’s activity from the previous day.

The ability to respond to unexpected behaviour is similarly concerning. Only 17.5% of respondents said their organisation could automatically stop an AI agent behaving unexpectedly in production. For the majority, intervention remains a manual process, potentially requiring an application to be taken offline.

“The data shows a gap that is already producing real operational consequences,” said Roey Eliyahu, CEO of Salt Security. “Organisations are deploying agents and granting them access to enterprise data, APIs, and services before they can trace what those agents are doing or stop them automatically when something goes wrong.”

Shadow AI Infrastructure and AI-Generated Code Raise Further Concerns

The report also identified emerging risks associated with Model Context Protocol (MCP) infrastructure, which enables AI systems to interact with external tools and data sources.

Nearly a third (32.9%) of respondents reported discovering an unauthorised, shadow or misconfigured MCP server in the past year, while 54.3% had either confirmed or suspected encountering one.

Salt Labs’ own telemetry revealed that MCP-related infrastructure was detected in 21.6% of customer environments in August 2026, compared with 16.7% in January, representing a relative increase of approximately 30%.

Meanwhile, AI-generated code is introducing additional application security challenges. Some 83.5% of respondents estimated that AI-generated or AI-assisted code contributed to at least some of their application security findings.

However, just 6.8% reported resolving these issues directly within coding assistants at the point of generation, leaving vulnerabilities to be identified during subsequent code reviews, testing or after deployment.

Recent Manus Vulnerability Highlights Agentic AI Risks

The findings follow recent research from Salt Labs, which demonstrated how a single malicious email could be used to hijack the Manus agentic AI platform and potentially access a user’s connected email, cloud storage and code repository accounts.

The attack did not require a stolen password or the victim to click a malicious link. Although the platform’s guardrails detected the malicious activity, they were unable to prevent the code from executing.

The vulnerability was responsibly disclosed and has since been remediated.

According to Salt Security, the incident demonstrates how traditional detection mechanisms may struggle to keep pace with autonomous systems capable of executing multiple actions before human intervention is possible.

“The Manus research and this survey data are two views of the same problem,” said Yaniv Balmas, Head of Research at Salt Security.

“In the field, we showed how an agent can be weaponised through a single malicious email, how the guardrail detected the attack at exactly the right moment, and still could not stop the code from running. The survey quantifies how widespread that architecture is.”

The findings underline the need for organisations to strengthen visibility into agent activity, establish appropriate governance controls and develop automated containment capabilities as AI agents gain greater autonomy and access to critical enterprise systems.

The full State of Agentic AI and API Security 2H 2026 report includes sector-specific findings, recommendations for CISOs and further analysis of Salt Labs production telemetry.

ShareTweet
Previous Post

Fake WatchGuard VPN site steals credentials, then serves the genuine signed client

Recent News

Nearly Half of Organisations Report Unauthorised AI Agent Actions, Research Finds

Nearly Half of Organisations Report Unauthorised AI Agent Actions, Research Finds

October 14, 2026
Fake WatchGuard VPN site steals credentials, then serves the genuine signed client

Fake WatchGuard VPN site steals credentials, then serves the genuine signed client

October 14, 2026
Check Point and Illumio Team Up to Advance Zero Trust with Unified Security and Threat Prevention

Zero Trust in Practice: Moving Beyond the Buzzword

October 14, 2026
Vega Appoints Category Builder Scott Simkin as Chief Marketing Officer to Define the Post-SIEM Era

Vega Appoints Category Builder Scott Simkin as Chief Marketing Officer to Define the Post-SIEM Era

October 14, 2026

Eskenzi PR banner ad

The IT Security Guru offers a daily news digest of all the best breaking IT security news stories first thing in the morning! Rather than you having to trawl through all the news feeds to find out what’s cooking, you can quickly get everything you need from this site!

Our Address: 10 London Mews, London, W2 1HY

Follow Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol

  • About Us
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
No Result
View All Result
  • Home
  • Features
  • Insight
  • Channel News
  • Events
    • Most Inspiring Women in Cyber 2026
  • Topics
    • Cloud Security
    • Cyber Crime
    • Cyber Warfare
    • Data Protection
    • DDoS
    • Hacking
    • Malware, Phishing and Ransomware
    • Mobile Security
    • Network Security
    • Regulation
    • Skills Gap
    • The Internet of Things
    • Threat Detection
    • AI and Machine Learning
    • Industrial Internet of Things
  • Multimedia
  • Product Reviews
  • About Us

© 2015 - 2026 IT Security Guru - Website Managed by Dessol